


Two Factor
Enable Two-Factor Authentication (2FA) using time-based one-time passwords (TOTP), email, and backup verification codes.

Safe pick
Yes — Two Factor is a safe, well-maintained plugin to use in 2026. It runs on 100K+ sites, is rated 4.8/5 and was last updated 2 months ago, and scores 88/100 on our health check.
- Proven at scale on 100K+ active sites
- Loved by users — 4.8/5 from 209 reviews
- Tested with the latest WordPress (7.1)
- Responsive support — 80% of recent threads resolved
How does it stack up?
Side-by-side on installs, updates, ratings & support

Daily downloads
Download spikes usually follow a new release — each site that auto-updates counts as a download.
Rankings
Where Two Factor stands todayWordPress.org search rankings
Live position in the plugin search, top 100| Keyword | Position |
|---|---|
| 2FA | #18 |
| authentication | #24 |
| MFA | #2 |
| security | #91 |
| totp | #3 |
Version adoption
Share of active sites per release.
Rating breakdown
★★★★★★★★★★ 4.8 from 209 reviews
About Two Factor
From the official readme · v0.17.0Description
The Two-Factor plugin adds an extra layer of security to your WordPress login by requiring users to provide a second form of authentication in addition to their password. This helps protect against unauthorized access even if passwords are compromised.
Setup Instructions
Important: Each user must individually configure their two-factor authentication settings.
For Individual Users
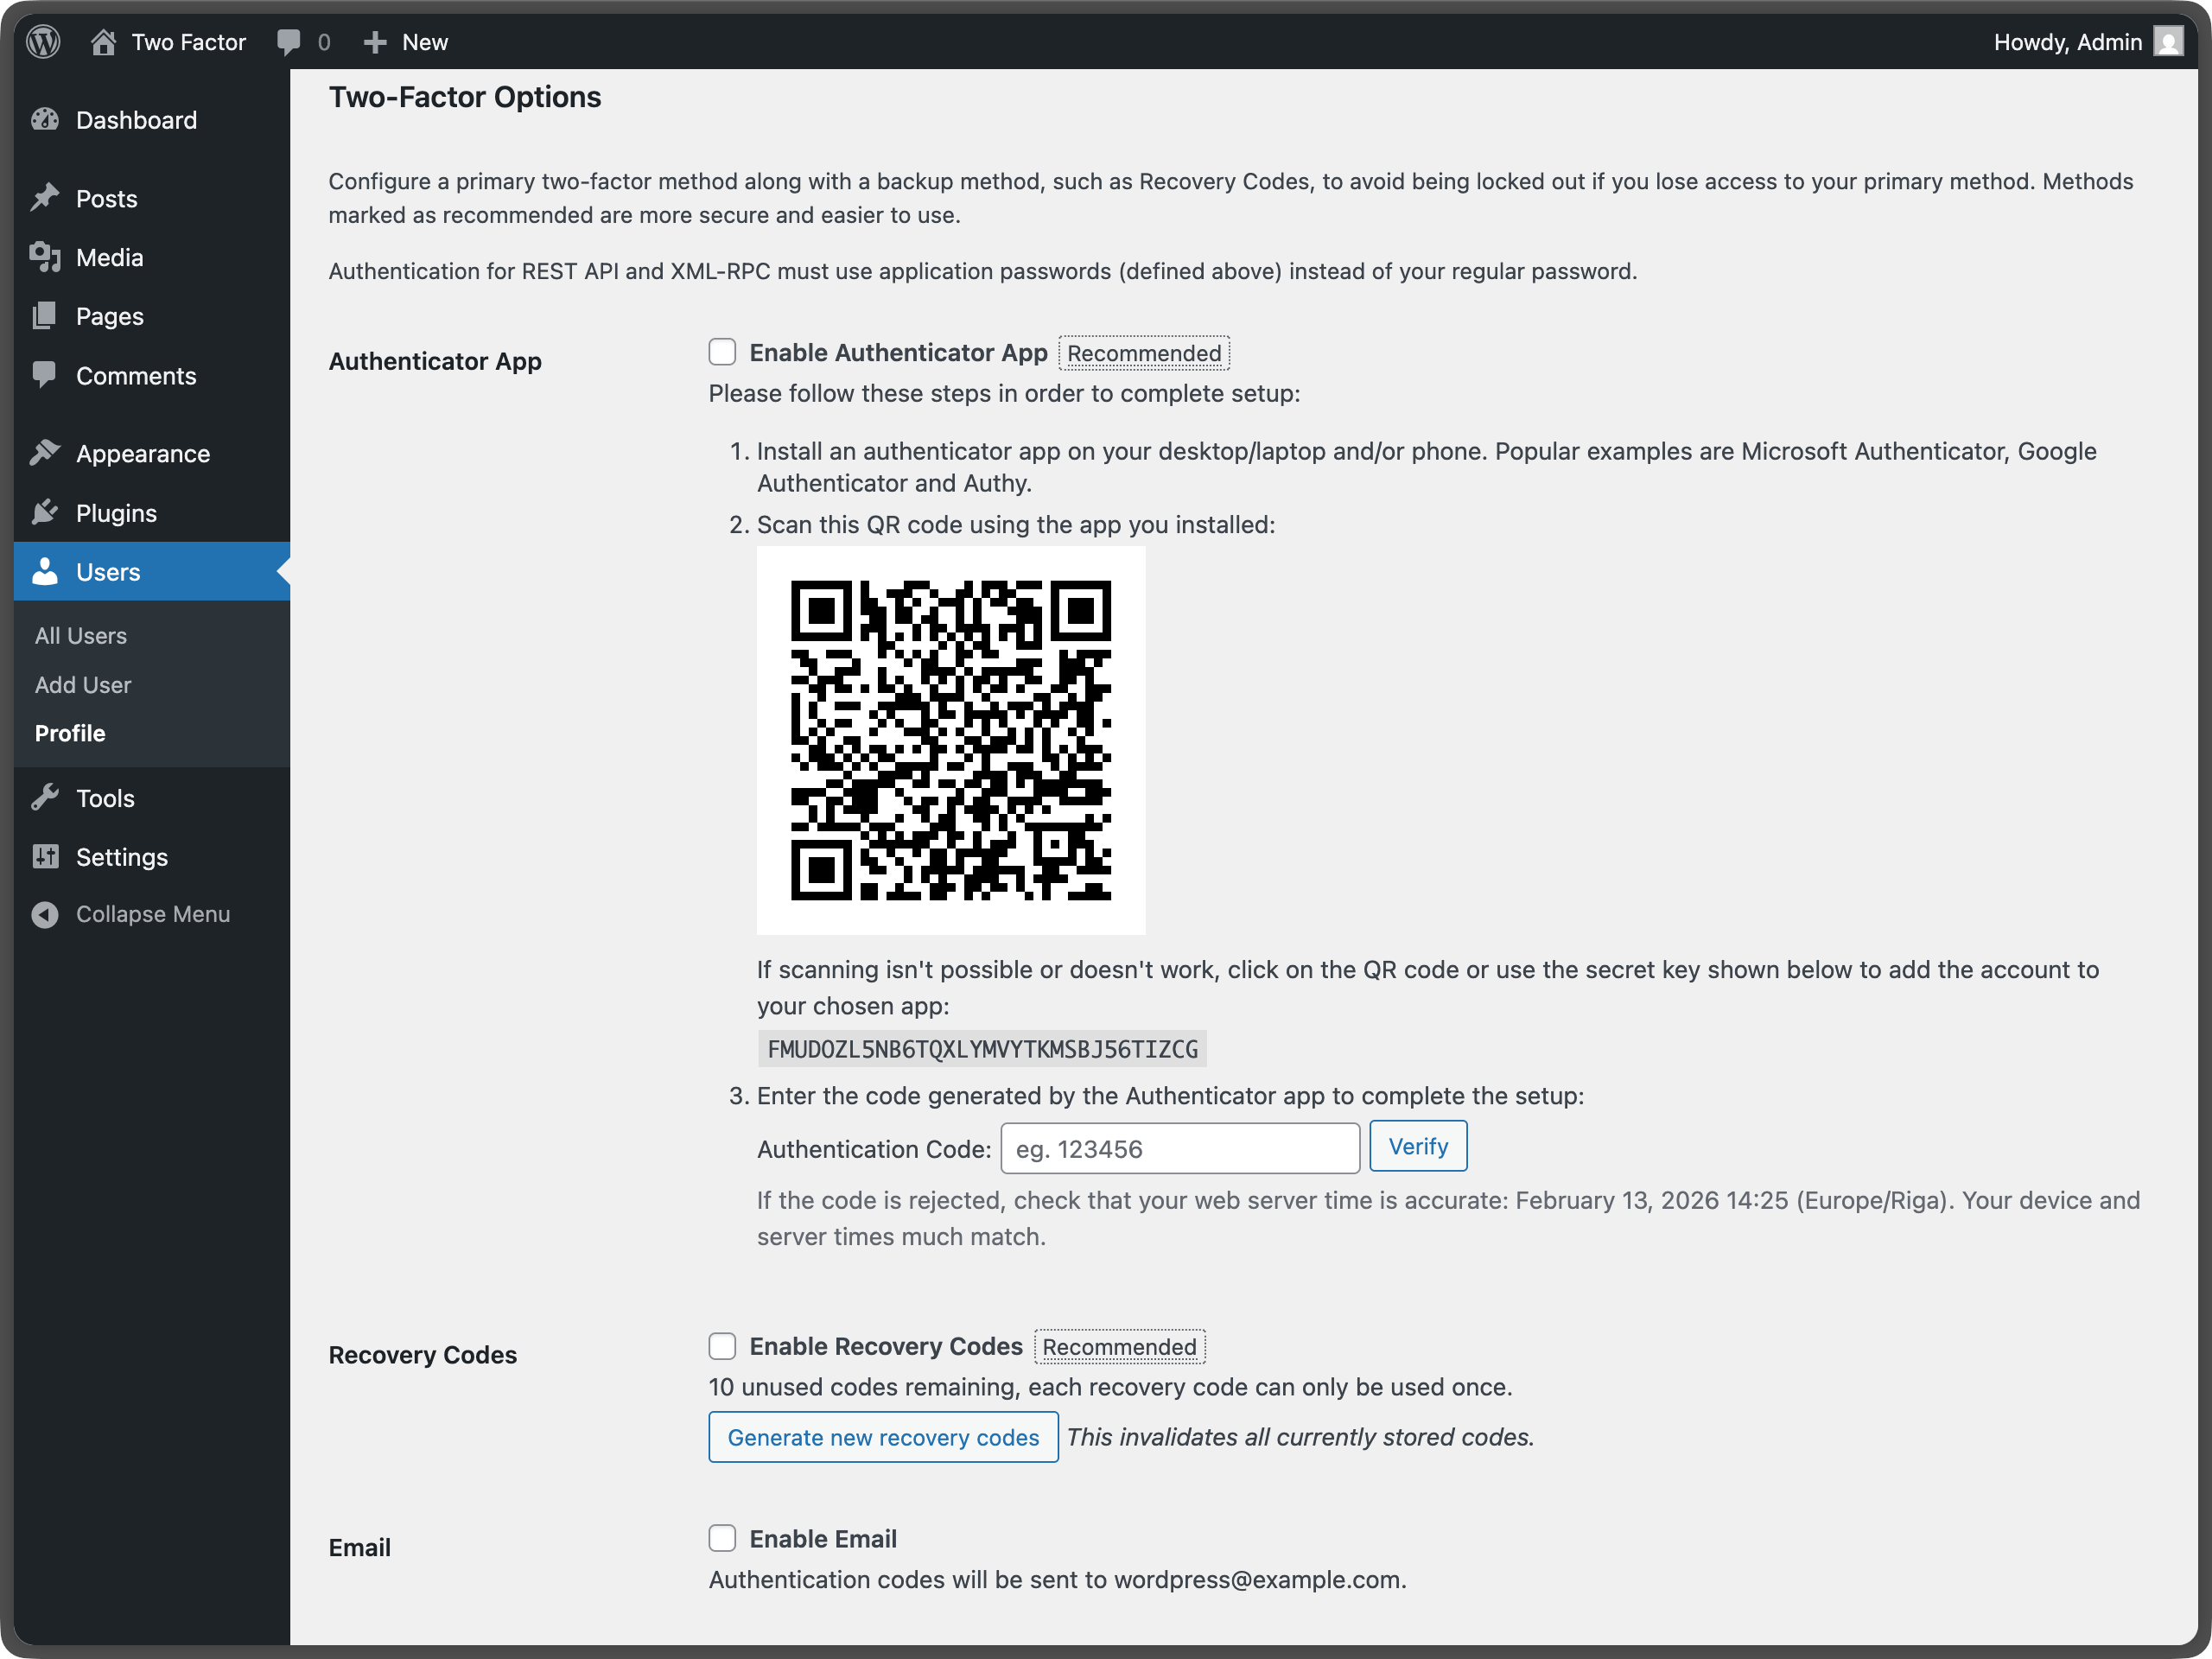
- Navigate to your profile: Go to “Users” → “Your Profile” in the WordPress admin
- Find Two-Factor Options: Scroll down to the “Two-Factor Options” section
- Choose your methods: Enable one or more authentication providers (noting a site admin may have hidden one or more so what is available could vary):
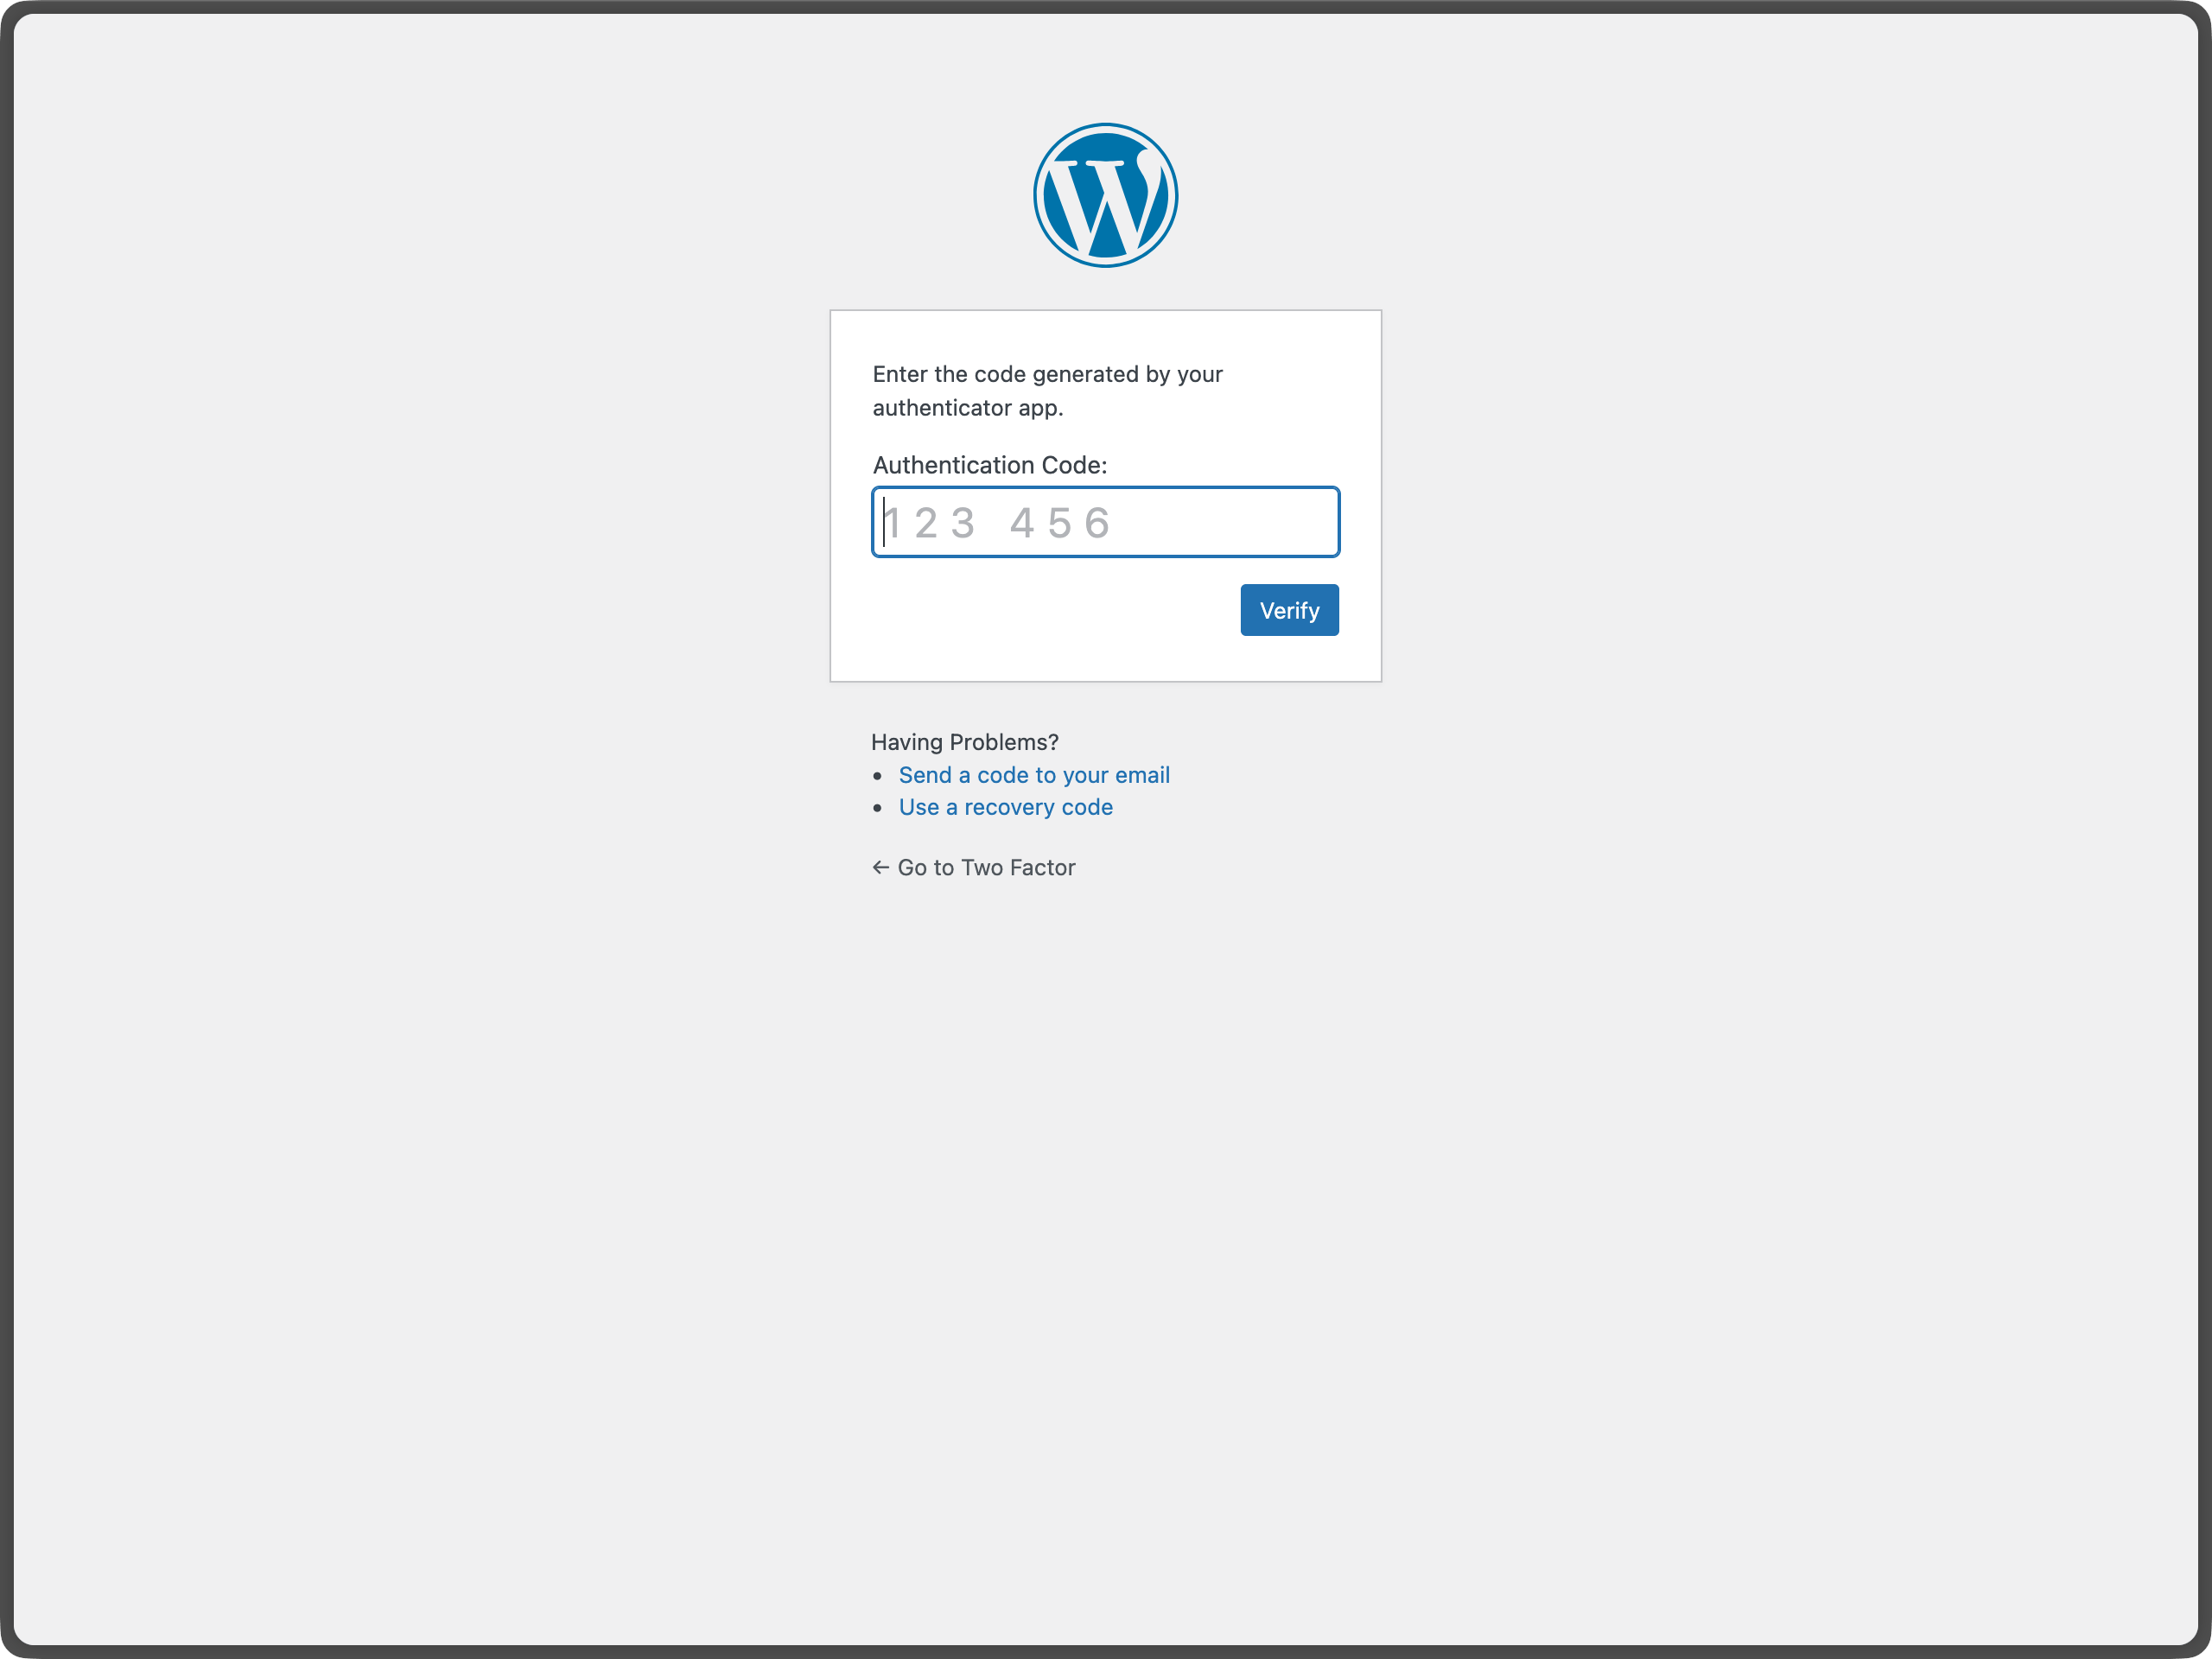
- Authenticator App (TOTP) – Use apps like Google Authenticator, Authy, or 1Password
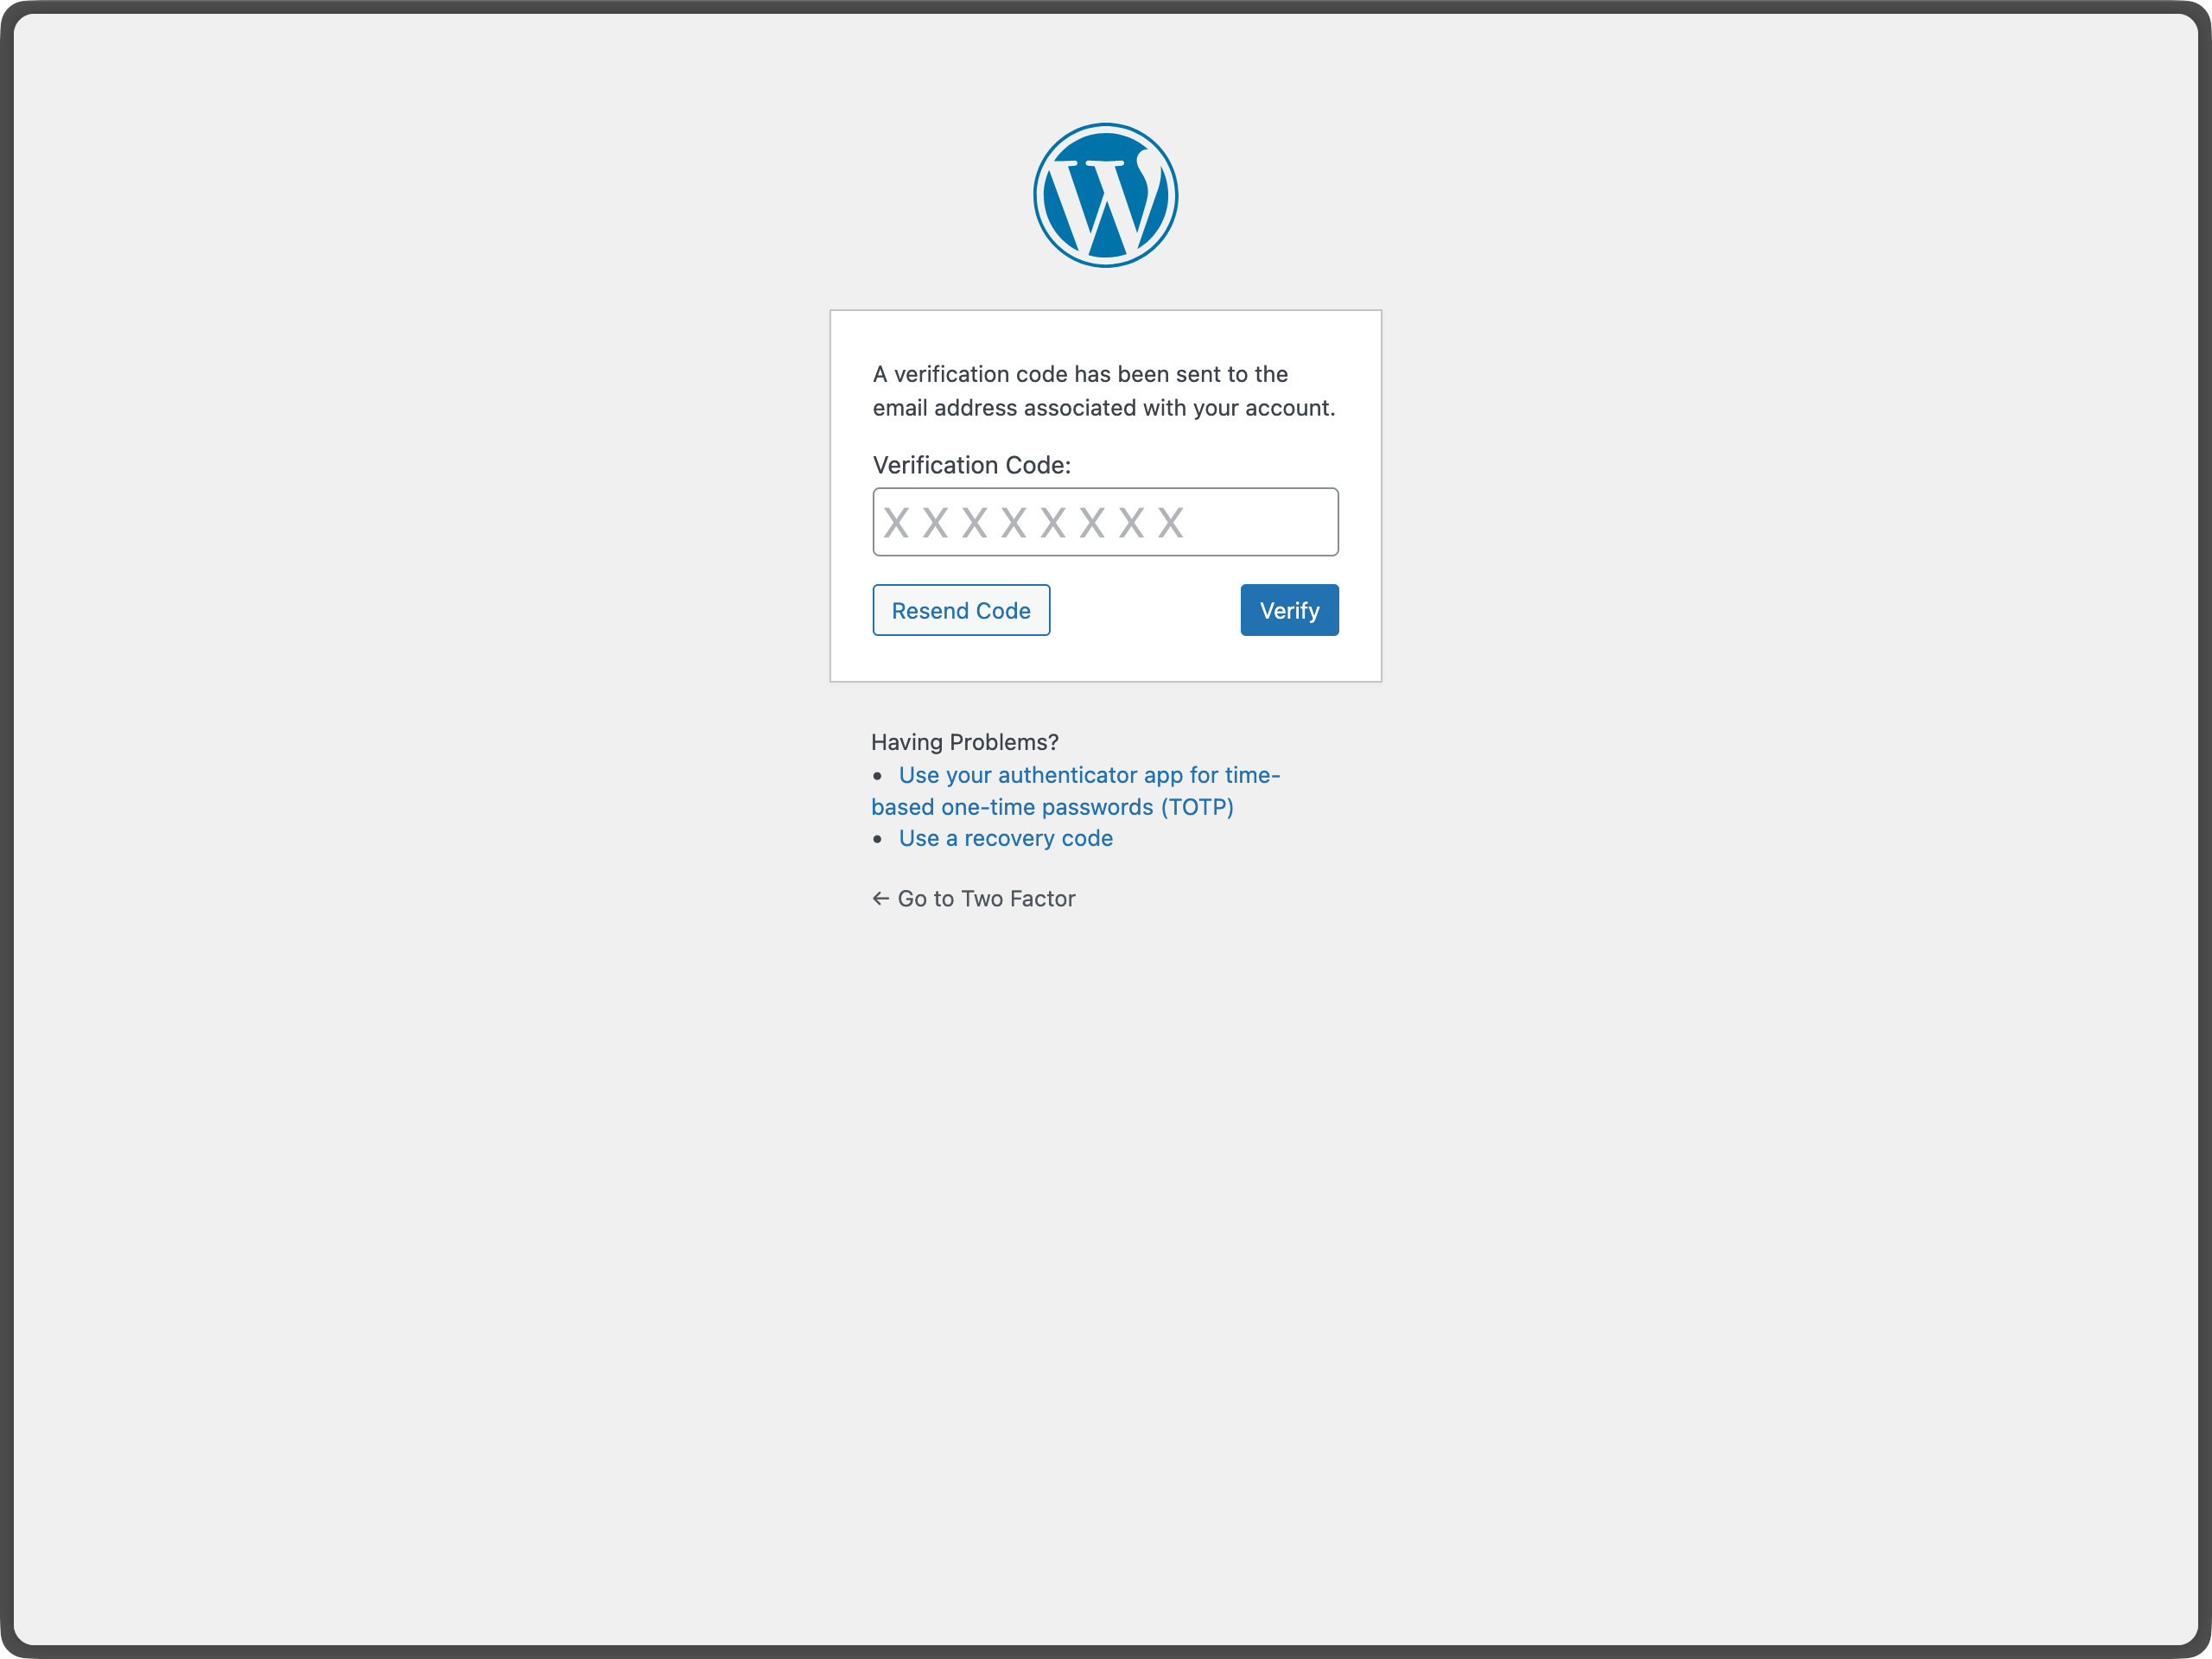
- Email Codes – Receive one-time codes via email
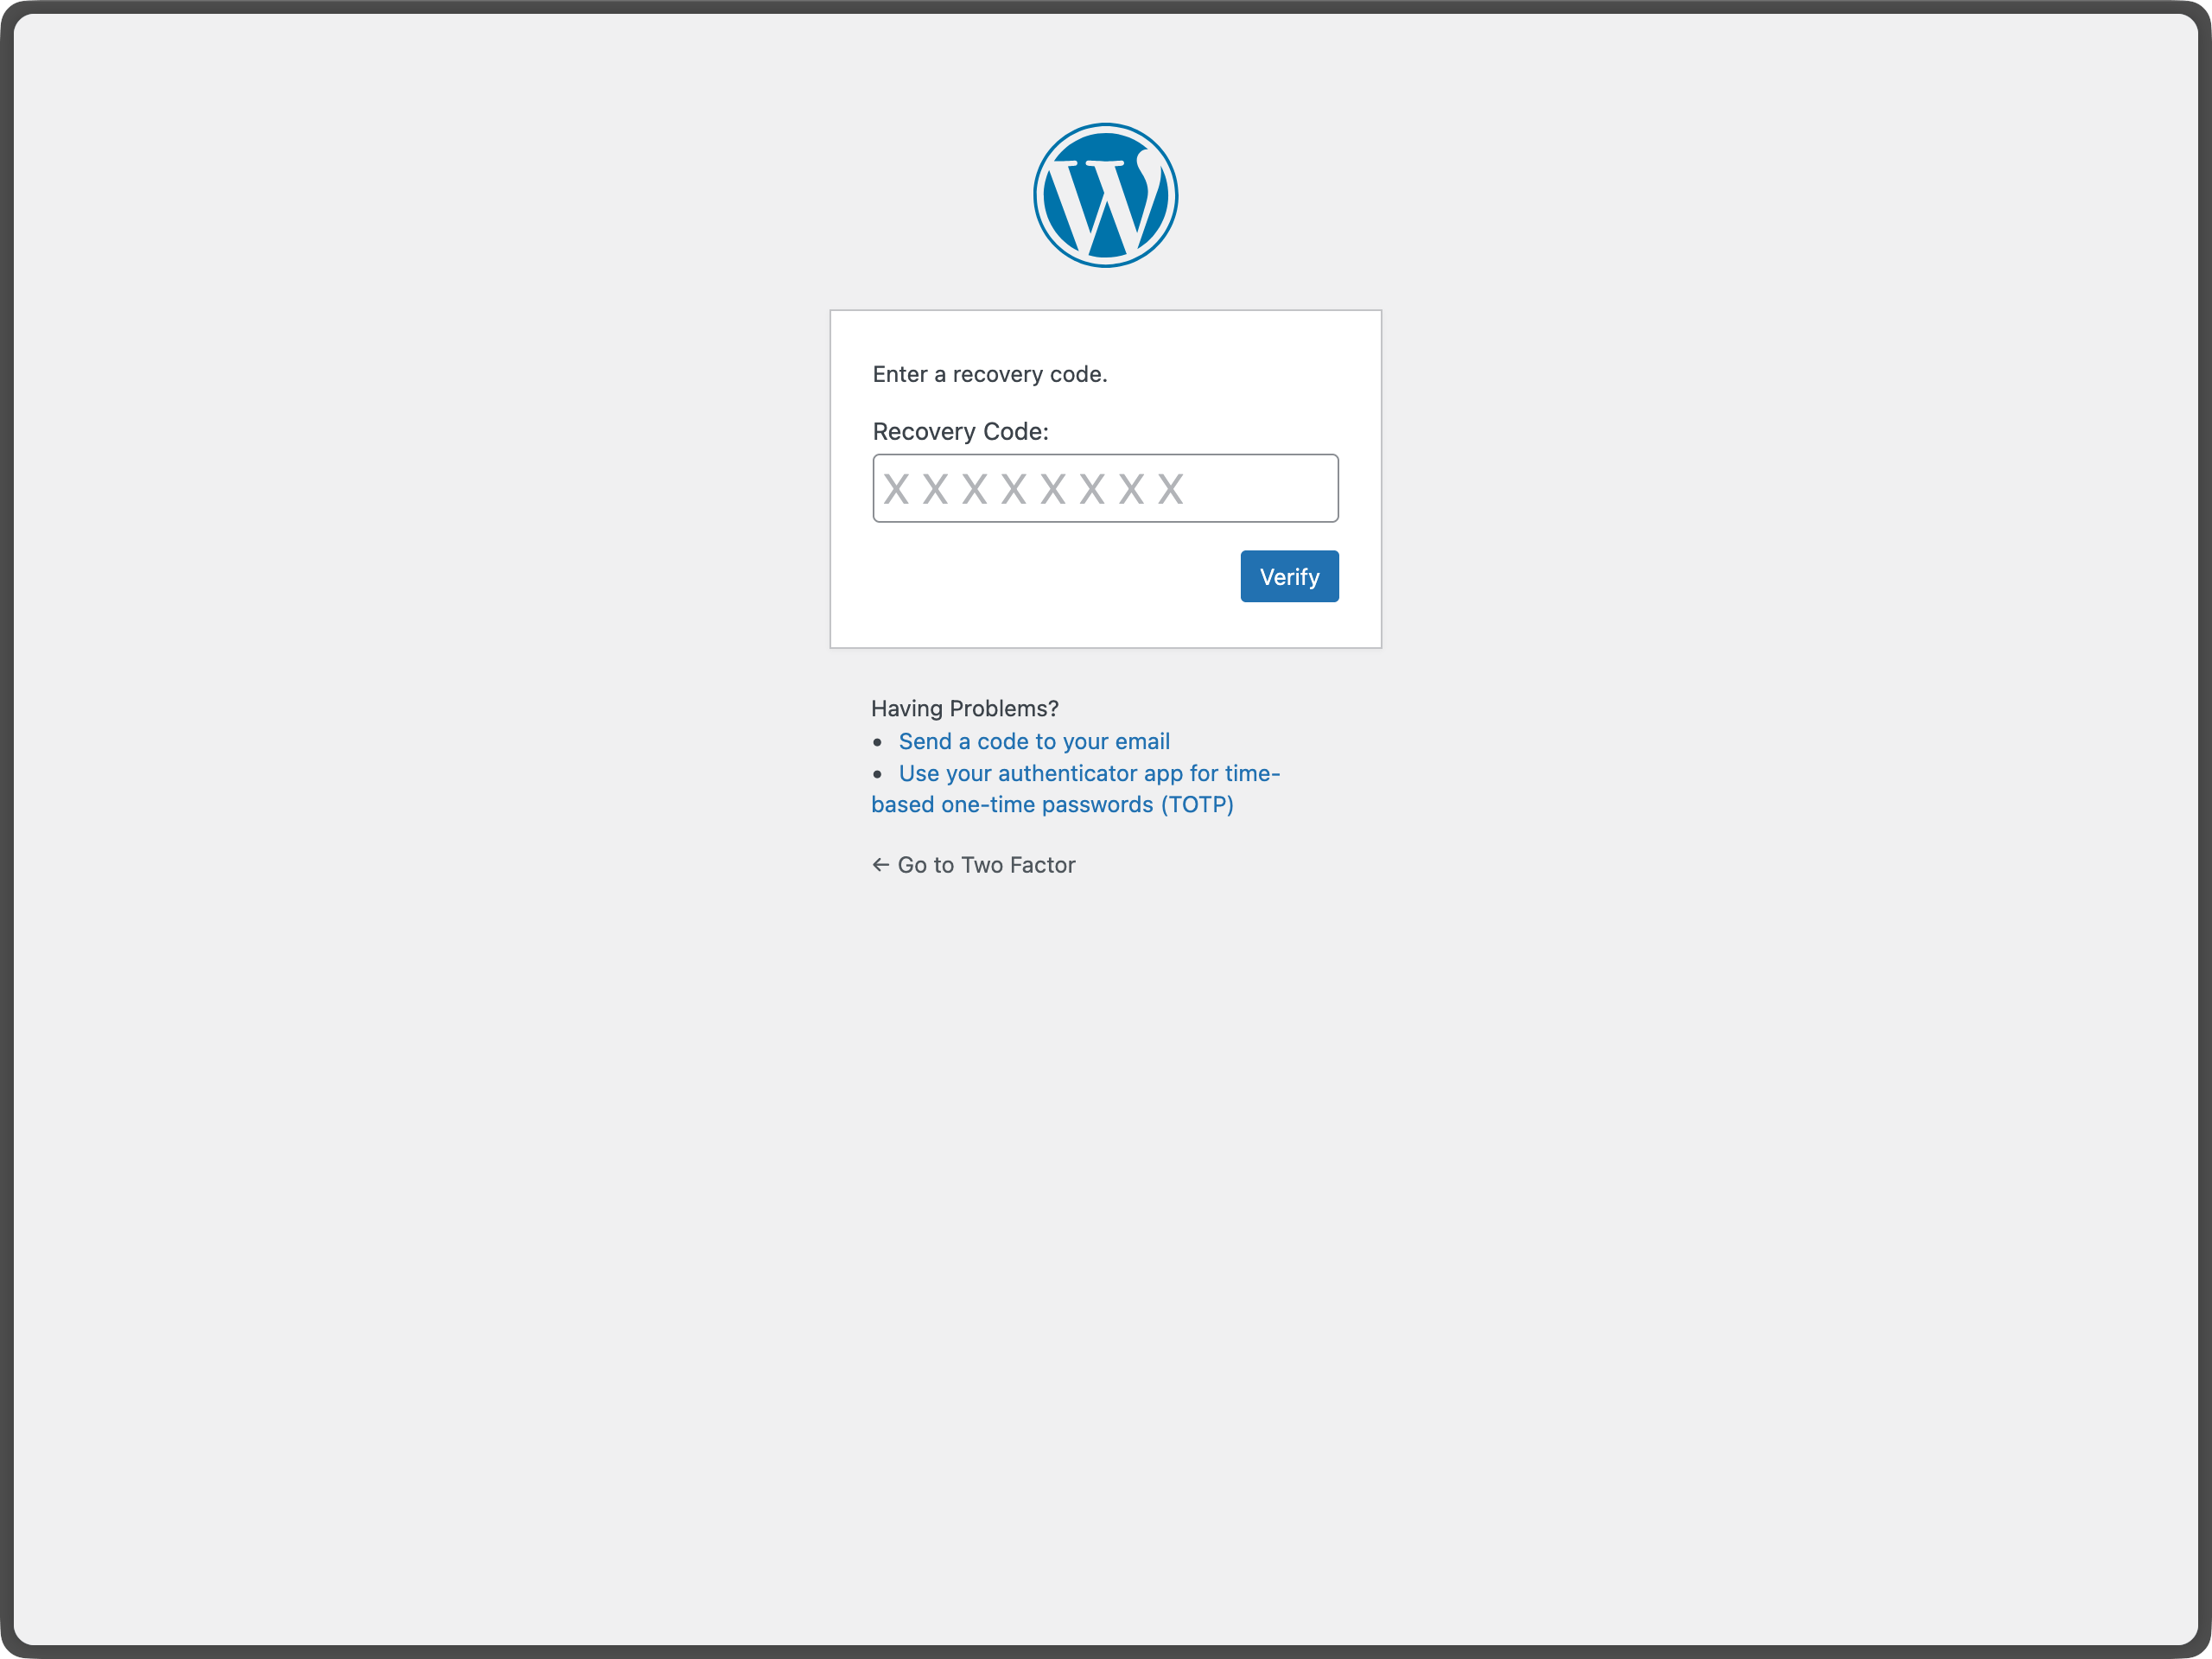
- Backup Codes – Generate one-time backup codes for emergencies
- Dummy Method – For testing purposes only (requires WP_DEBUG)
- Configure each method: Follow the setup instructions for each enabled provider
- Set primary method: Choose which method to use as your default authentication
- Save changes: Click “Update Profile” to save your settings
For Site Administrators
- Plugin settings: The plugin provides a settings page under “Settings → Two-Factor” to configure which providers should be disabled site-wide.
- User management: Administrators can configure 2FA for other users by editing their profiles
- Security recommendations: Encourage users to enable backup methods to prevent account lockouts
Available Authentication Methods
Authenticator App (TOTP) – Recommended
- Security: High – Time-based one-time passwords
- Setup: Scan QR code with authenticator app
- Compatibility: Works with Google Authenticator, Authy, 1Password, and other TOTP apps
- Best for: Most users, provides excellent security with good usability
Backup Codes – Recommended
- Security: Medium – One-time use codes
- Setup: Generate 10 backup codes for emergency access
- Compatibility: Works everywhere, no special hardware needed
- Best for: Emergency access when other methods are unavailable
Email Codes
- Security: Medium – One-time codes sent via email
- Setup: Automatic – uses your WordPress email address
- Compatibility: Works with any email-capable device
- Best for: Users who prefer email-based authentication
FIDO U2F Security Keys
- Deprecated and removed due to loss of browser support.
Dummy Method
- Security: None – Always succeeds
- Setup: Only available when WP_DEBUG is enabled
- Purpose: Testing and development only
- Best for: Developers testing the plugin
Important Notes
HTTPS Requirement
- All methods work on both HTTP and HTTPS sites
Browser Compatibility
- TOTP and email methods work on all devices and browsers
Account Recovery
- Always enable backup codes to prevent being locked out of your account
- If you lose access to all authentication methods, contact your site administrator
Security Best Practices
- Use multiple authentication methods when possible
- Keep backup codes in a secure location
- Regularly review and update your authentication settings
For more information about two-factor authentication in WordPress, see the WordPress Advanced Administration Security Guide.
For more history, see this post.
Actions & Filters
Here is a list of action and filter hooks provided by the plugin:
two_factor_providersfilter overrides the available two-factor providers such as email and time-based one-time passwords. Array values are PHP classnames of the two-factor providers.two_factor_providers_for_userfilter overrides the available two-factor providers for a specific user. Array values are instances of provider classes and the user objectWP_Useris available as the second argument.two_factor_enabled_providers_for_userfilter overrides the list of two-factor providers enabled for a user. First argument is an array of enabled provider classnames as values, the second argument is the user ID.two_factor_is_required_for_userfilter controls whether two-factor authentication is required for a user. Returnfalseto bypass the two-factor flow (e.g. for trusted IP addresses). First argument is a boolean (whether the user has a primary provider configured), the second argument is theWP_Userobject.two_factor_fallback_provider_for_userfilter overrides the provider forced on when none of a user’s stored two-factor providers are still registered (e.g. after a provider plugin is deactivated). Defaults toTwo_Factor_Email. First argument is the provider classname, the second is the user ID, the third is the array of provider classnames that were stored for the user but are no longer registered. The returned provider must be registered and available to the user (is_available_for_user()), or the user is shown an error instead of being let through with a fallback.two_factor_user_authenticatedaction which receives the logged inWP_Userobject as the first argument for determining the logged in user right after the authentication workflow.two_factor_user_api_login_enablefilter restricts authentication for REST API and XML-RPC to application passwords only. Provides the user ID as the second argument.two_factor_email_token_ttlfilter overrides the time interval in seconds that an email token is considered after generation. Accepts the time in seconds as the first argument and the ID of theWP_Userobject being authenticated.two_factor_email_token_lengthfilter overrides the default 8 character count for email tokens.two_factor_backup_code_lengthfilter overrides the default 8 character count for backup codes. Provides theWP_Userof the associated user as the second argument.two_factor_rest_api_can_edit_userfilter overrides whether a user’s Two-Factor settings can be edited via the REST API. First argument is the current$can_editboolean, the second argument is the user ID.two_factor_before_authentication_promptaction which receives the provider object and fires prior to the prompt shown on the authentication input form.two_factor_after_authentication_promptaction which receives the provider object and fires after the prompt shown on the authentication input form.two_factor_after_authentication_inputaction which receives the provider object and fires after the input shown on the authentication input form (if form contains no input, action fires immediately aftertwo_factor_after_authentication_prompt).two_factor_login_backup_linksfilters the backup links displayed on the two-factor login form.two_factor_login_nonce_failedaction which fires when a login nonce fails verification. Provides the ID of the user the nonce was presented for as the first argument, and the reason as the second:no_nonce_stored,expired, ormismatch.two_factor_log_login_nonce_failuresfilter overrides whether a failed login nonce verification is written to the PHP error log. Defaults to true forexpiredandmismatch, and false forno_nonce_stored, which any unauthenticated request can reach. Provides the user ID as the second argument and the reason as the third.
WP-CLI Commands
The plugin includes a wp two-factor WP-CLI namespace for managing two-factor authentication from the command line. All commands accept a user by ID, login, or email.
wp two-factor status <user>— Shows a user’s current 2FA status (read-only). Supports--format=json.wp two-factor list-providers— Lists all registered two-factor providers.wp two-factor enable <user> <provider>— Enables a provider for a user. Providers that require a shared secret (like TOTP) can’t be enabled this way and will point you to the profile page instead.wp two-factor disable <user> [<provider>]— Disables a single provider, or performs a full reset of all 2FA for the user when no provider is given. Both forms prompt for confirmation unless--yesis passed.wp two-factor backup-codes generate <user> [--count=<n>]— Generates a fresh set of backup codes for a user, replacing any existing ones. Defaults to 10 codes.wp two-factor unlock <user>— Clears a user’s login rate-limit/throttle without changing their 2FA configuration.
Run wp help two-factor for the full list, or wp help two-factor <command> for options and examples for a specific command.
Redirect After the Two-Factor Challenge
To redirect users to a specific URL after completing the two-factor challenge, use WordPress Core built-in login_redirect filter. The filter works the same way as in a standard WordPress login flow:
add_filter( 'login_redirect', function( $redirect_to, $requested_redirect_to, $user ) {
    return home_url( '/dashboard/' );
}, 10, 3 );
Changelog
Bumps WordPress minimum supported version to 6.3 and PHP minimum to 7.2.
0.17.0 – 2026-09-25
- Security Fixes: Ensure that regular passwords can’t bypass the two-factor requirement for REST API and XML-RPC requests by @faisalahammad in #989. Thanks mqrble for responsibly reporting the issue.
- Security Fixes: Add diagnostics for failed login nonce verification by @georgestephanis in #973. Thanks Ananda Dhakal (Patchstack) for responsibly reporting the issue.
- New Features: Add WP-CLI support with
wp two-factorcommands by @masteradhoc in #905 - New Features: Respect intentional bypass via the
two_factor_is_required_for_userfilter by @masteradhoc in #882 - New Features: Add a
two_factor_fallback_provider_for_userfilter for when a user’s stored providers are no longer registered by @masteradhoc in #882 - New Features: Add early notice for soon exhausting recovery codes by @masteradhoc in #907
- New Features: Add privacy policy content registration by @masteradhoc in #869
- Bug Fixes: Fail closed when CSPRNG is unavailable during nonce generation by @dknauss in #877
- Bug Fixes: Only clear the login nonce once it has expired by @georgestephanis in #980
- Bug Fixes: Fix unslashed
REMOTE_ADDRwarning in email provider by @masteradhoc in #975 - Bug Fixes: Fix TOTP verify button after resetting authenticator app by @lakrisgubben in #979
- Bug Fixes: Remove
two_factor_enabled_providersoption on uninstall by @faisalahammad in #903 - Bug Fixes: Fix misleading notice by @masteradhoc in #858
- Bug Fixes: Reword mixed-audience login failure notice to be informational by @dknauss in #922
- Bug Fixes: Rework fail-safe by @masteradhoc in #927
- Bug Fixes: Add coverage for provider-specific fallback notices by @dknauss in #923
- Bug Fixes: Fix HTML5 validation issues by @masteradhoc in #910
- Bug Fixes: Fix users list table fatals (
wp_die) when a user’s 2FA provider is deregistered by @masteradhoc in #933 - Development Updates: Prepare for the WordPress 7.0 release by @masteradhoc in #834
- Development Updates: Prepare for the WordPress 7.1 release by @masteradhoc in #900
- Development Updates: Sync
login_header()andlogin_footer()with WP 7.1 by @masteradhoc in #963 - Development Updates: Update PHPStan to 2.x and exclude
includes/from analysis by @masteradhoc in #972 - Development Updates: Validate against PHPStan version 3, 4 and 5 by @masteradhoc in #948
- Development Updates: Update
wp-coding-standards/wpcsto 3.4.1 by @obenland in #947 - Development Updates: Fix PHPCS and PHPStan issues across multiple files by @aslamdoctor in #818
- Development Updates: Remove
ReflectionProperty::setAccessible()andReflectionMethod::setAccessible()calls in the test suite by @masteradhoc in #942 - Development Updates: Fix Codecov badge by adding OIDC permission for tokenless upload by @nimesh-xecurify in #856
- Development Updates: Update GitHub Actions workflows by @johnbillion in #892
- Development Updates: Update Playground PR preview action to v4 by @obenland in #985
- Development Updates: Add FAQ entries for Multisite, locked-out users, and role enforcement by @masteradhoc in #881
- Development Updates: Update
.mdfiles with the latest two-factor changes and requirements by @masteradhoc in #929 - Development Updates: Update PR template by @masteradhoc in #870
- Development Updates: Unbreak CI: PHPStan false positive and matrix fail-fast by @georgestephanis in #974
- Dependency Updates: Bump the
qrcode-generatorruntime dependency by @kasparsd - Dependency Updates: Bump
qsandexpressby @dependabot[bot] in #895 - Dependency Updates: Bump adm-zip and
@wordpress/scriptsby @dependabot[bot] in #988
0.16.0 – 2026-03-27
- Breaking Changes: Remove legacy FIDO U2F provider support by #439.
- New Features: Add a dedicated settings page for plugin configuration in wp-admin by #764.
- New Features: Add a support links filter so consumers can customize contextual recovery/help links by #615.
- New Features: Refresh backup codes UI styling and behavior by #804.
- Bug Fixes: Delete stored TOTP secrets when the TOTP provider is disabled by #802.
- Bug Fixes: Harden provider handling so login/settings checks do not fail open when expected providers disappear by #586.
- Bug Fixes: Ensure only configured providers are saved and enabled in user settings by #798.
- Bug Fixes: Improve settings-page accessibility and fix profile settings link behavior by #828 and #830.
- Bug Fixes: Resolve PHPCS violations in provider files by #851.
- Development Updates: Move login styles and provider scripts from inline output to enqueued/external assets by #807 and #814.
- Development Updates: Improve inline docs and static-analysis compatibility (WPCS/phpstan) by #810, #815, and #817.
- Development Updates: Improve unit test reliability and integrate CI code coverage reporting by #825, #841, and #842.
- Development Updates: Update readme docs and modernize CI workflow infrastructure by #835, #837, #843, and #849.
- Dependency Updates: Bump
qsfrom 6.14.1 to 6.14.2 by #794. - Dependency Updates: Bump
basic-ftpfrom 5.0.5 to 5.2.0 by #816. - Dependency Updates: Apply automatic lint/format updates and associated Composer package refreshes by #799.
0.15.0 – 2026-02-13
- Breaking Changes: Trigger two-factor flow only when expected by @kasparsd in #660 and #793.
- New Features: Include user IP address and contextual warning in two-factor code emails by @todeveni in #728
- New Features: Optimize email text for TOTP by @masteradhoc in #789
- New Features: Add “Settings” action link to plugin list for quick access to profile by @hardikRathi in #740
- New Features: Additional form hooks by @eric-michel in #742
- New Features: Full RFC6238 Compatibility by @ericmann in #656
- New Features: Consistent user experience for TOTP setup by @kasparsd in #792
- Documentation:
@sincedocs by @masteradhoc in #781 - Documentation: Update user and admin docs, prepare for more screenshots by @jeffpaul in #701
- Documentation: Add changelog & credits, update release notes by @jeffpaul in #696
- Documentation: Clear readme.txt by @masteradhoc in #785
- Documentation: Add date and time information above TOTP setup instructions by @masteradhoc in #772
- Documentation: Clarify TOTP setup instructions by @masteradhoc in #763
- Documentation: Update RELEASING.md by @jeffpaul in #787
- Development Updates: Pause deploys to SVN trunk for merges to
masterby @kasparsd in #738 - Development Updates: Fix CI checks for PHP compatability by @kasparsd in #739
- Development Updates: Fix Playground refs by @kasparsd in #744
- Development Updates: Persist existing translations when introducing new helper text in emails by @kasparsd in #745
- Development Updates: Fix
missing_direct_file_access_protectionby @masteradhoc in #760 - Development Updates: Fix
mismatched_plugin_nameby @masteradhoc in #754 - Development Updates: Introduce Props Bot workflow by @jeffpaul in #749
- Development Updates: Plugin Check: Fix Missing $domain parameter by @masteradhoc in #753
- Development Updates: Tests: Update to supported WP version 6.8 by @masteradhoc in #770
- Development Updates: Fix PHP 8.5 deprecated message by @masteradhoc in #762
- Development Updates: Exclude 7.2 and 7.3 checks against trunk by @masteradhoc in #769
- Development Updates: Fix Plugin Check errors:
MissingTranslatorsComment&MissingSingularPlaceholderby @masteradhoc in #758 - Development Updates: Add PHP 8.5 tests for latest and trunk version of WP by @masteradhoc in #771
- Development Updates: Add
phpcs:ignorefor falsepositives by @masteradhoc in #777 - Development Updates: Fix(totp):
otpauthlink in QR code URL by @sjinks in #784 - Development Updates: Update deploy.yml by @masteradhoc in #773
- Development Updates: Update required WordPress Version by @masteradhoc in #765
- Development Updates: Fix: ensure execution stops after redirects by @sjinks in #786
- Development Updates: Fix
WordPress.Security.EscapeOutput.OutputNotEscapederrors by @masteradhoc in #776 - Dependency Updates: Bump qs and express by @dependabot[bot] in #746
- Dependency Updates: Bump lodash from 4.17.21 to 4.17.23 by @dependabot[bot] in #750
- Dependency Updates: Bump lodash-es from 4.17.21 to 4.17.23 by @dependabot[bot] in #748
- Dependency Updates: Bump phpunit/phpunit from 8.5.44 to 8.5.52 by @dependabot[bot] in #755
- Dependency Updates: Bump symfony/process from 5.4.47 to 5.4.51 by @dependabot[bot] in #756
- Dependency Updates: Bump qs and body-parser by @dependabot[bot] in #782
- Dependency Updates: Bump webpack from 5.101.3 to 5.105.0 by @dependabot[bot] in #780
0.14.2 – 2025-12-11
- New Features: Add filter for rest_api_can_edit_user_and_update_two_factor_options by @gutobenn in #689
- Development Updates: Remove Coveralls tooling and add inline coverage report by @kasparsd in #717
- Development Updates: Update blueprint path to pull from main branch instead of a deleted f… by @georgestephanis in #719
- Development Updates: Fix blueprint and wporg asset deploys by @kasparsd in #734
- Development Updates: Upload release only on tag releases by @kasparsd in #735
- Development Updates: Bump playwright and @playwright/test by @dependabot[bot] in #721
- Development Updates: Bump tar-fs from 3.1.0 to 3.1.1 by @dependabot[bot] in #720
- Development Updates: Bump node-forge from 1.3.1 to 1.3.2 by @dependabot[bot] in #724
- Development Updates: Bump js-yaml by @dependabot[bot] in #725
- Development Updates: Mark as tested with the latest WP core version by @kasparsd in #730
0.14.1 – 2025-09-05
- Don’t URI encode the TOTP url for display. by @dd32 in #711
- Removed the duplicate Security.md by @slvignesh05 in #712
- Fixed linting issues by @sudar in #707
- Update development dependencies and fix failing QR unit test by @kasparsd in #714
- Trigger checkbox js change event by @gedeminas in #688
0.14.0 – 2025-07-03
- Features: Enable Application Passwords for REST API and XML-RPC authentication (by default) by @joostdekeijzer in #697 and #698. Previously this required two_factor_user_api_login_enable filter to be set to true which is now the default during application password auth. XML-RPC login is still disabled for regular user passwords.
- Features: Label recommended methods to simplify the configuration by @kasparsd in #676 and #675
- Documentation: Add WP.org plugin demo by @kasparsd in #667
- Documentation: Document supported versions of WP core and PHP by @jeffpaul in #695
- Documentation: Document the release process by @jeffpaul in #684
- Tooling: Remove duplicate WP.org screenshots and graphics from SVN trunk by @jeffpaul in #683
Screenshots
For developers
Is this your plugin? Show off the numbers.
Add a live badge to your site, docs or GitHub README. It updates on its own — no account needed.
Best Two Factor alternatives
All 2FA plugins →


FAQ
Two Factor: quick answers
Straight answers, pulled from live WordPress.org data.
Live data from WordPress.org · checked Nov 17, 2026
Is Two Factor free?
Yes. Two Factor is free to download and use from the official WordPress.org plugin directory.
Is Two Factor safe to use in 2026?
Yes — Two Factor is a safe, well-maintained plugin to use in 2026. It runs on 100K+ sites, is rated 4.8/5 and was last updated 2 months ago, and scores 88/100 on our health check.
How many websites use Two Factor?
Two Factor is active on 100K+ WordPress websites and has been downloaded 2,058,511 times since it launched in August 2015. It was downloaded 132,621 times in the last 30 days.
Does Two Factor work with WordPress 7.1?
Yes. The developer has tested Two Factor up to WordPress 7.1.4, the latest release. It requires WordPress 7.0 or newer.
What PHP version does Two Factor need?
Two Factor requires PHP 7.4 or higher. Most hosts run PHP 8.x today, so it works on any modern WordPress hosting.
When was Two Factor last updated?
The latest version, 0.17.0, was released on September 28, 2026 (2 months ago).
Who makes Two Factor?
Two Factor is developed and maintained by WordPress.org.
What are the best alternatives to Two Factor?
The most popular alternatives to Two Factor are Wordfence Security (5M+ installs), Really Simple Security (3M+ installs) and Limit Login Attempts Securi… (1M+ installs).
Powered by PageForge
Want thousands of pages that rank like these? Build them in an afternoon.
This directory runs on the same engine as PageForge. Turn any spreadsheet, CSV or API into thousands of fast, SEO-ready WordPress pages — with schema, internal links and AI-written copy baked in.
- CSV, Google Sheets & API data sources
- AI content, schema & internal links per page
- Works with Elementor, Gutenberg, Yoast & Rank Math
- Free on WordPress.org — no credit card


