

Champlin Pre-Flight Audit
Premium pre-flight (and post-flight) audit for the WordPress 7.0 upgrade. 30+ automated checks. Visual readiness score. Free.

Use with caution
Champlin Pre-Flight Audit works, but test it on a staging site before relying on it in 2026. Was last updated 3 months ago, and scores 49/100 on our health check.
- Small user base (<10 active installs)
- Very few reviews so far
How does it stack up?
Side-by-side on installs, updates, ratings & support
Daily downloads
Download spikes usually follow a new release — each site that auto-updates counts as a download.
Rankings
Where Champlin Pre-Flight Audit stands todayWordPress.org search rankings
Live position in the plugin search, top 100| Keyword | Position |
|---|---|
| audit | >100 |
| compatibility | >100 |
| enterprise | >100 |
| readiness | >100 |
| upgrade | >100 |
About Champlin Pre-Flight Audit
From the official readme · v1.0.7Description
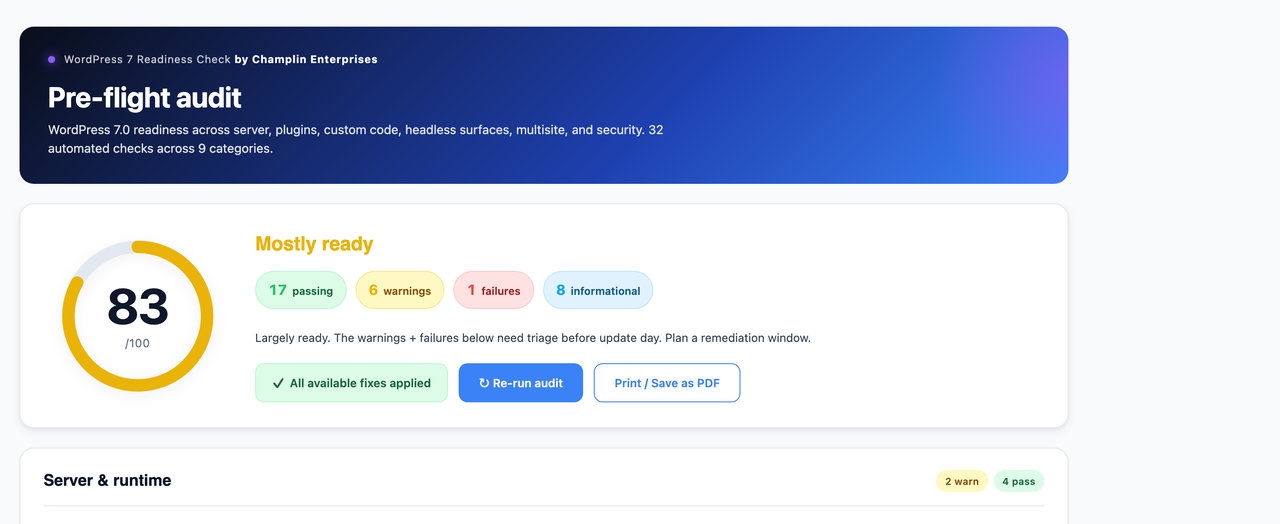
The WordPress 7.0 upgrade is the biggest core release in years — bringing the WP AI Client, DataViews, Block API v3, and a higher PHP floor. This plugin runs a 30+ point automated audit of your site against the WordPress 7.0 readiness criteria, with a visual score and remediation hints for every finding.
The same checks the engineering team at Champlin Enterprises runs across enterprise WordPress migrations, packaged free for the community.
About this distribution
This is the WordPress.org distribution of the plugin. A self-hosted variant is available at https://github.com/Kevinchamplin/champlin-pre-flight-audit for users who prefer to install directly from GitHub. The audit logic, autofixes, and snapshot system are identical; only the update mechanism differs.
What it checks
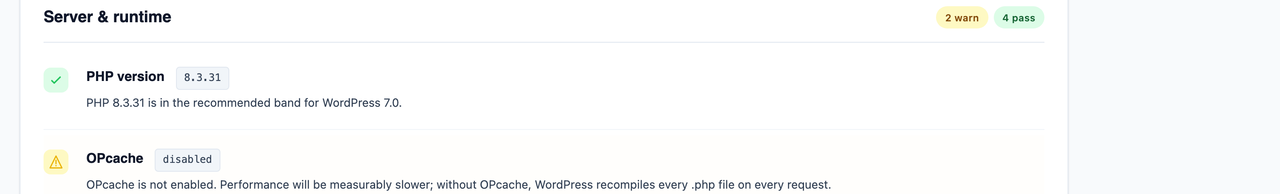
- Server & runtime — PHP version, OPcache, memory limit, max_execution_time, required extensions
- Database — MySQL/MariaDB version, InnoDB availability
- WordPress core — version, debug mode, auto-update status, HTTPS
- Plugins — pending updates, per-plugin compatibility headers, known-risky page-builder slugs
- Themes — active theme version, compatibility header, block vs classic, deprecated theme support
- Custom code — static scan of your theme + custom plugins for WordPress 7.0 breaking patterns (WP_List_Table, manage_posts_columns, Block API v2, Interactivity effect(), deprecated HTML5 script support, and more)
- Headless & API — WPGraphQL detection, custom REST routes
- Multisite — site count, super admins, 7.0 spam-flag behavior change
- Security — admin user count, 2FA plugin, backup plugin, file-edit lockdown, AI Connectors policy reminder
What it does NOT do
- It does not modify your site. Read-only.
- It does not phone home or transmit any data externally.
- It does not require a license key or account signup.
Why it’s free
This plugin is the automated companion to the 80-point printable enterprise readiness checklist published by Champlin Enterprises at champlinenterprises.com/wordpress-7-0-readiness-checklist.html. Together they cover the engineering work of a WordPress 7.0 migration. If you’d rather have an engineer run it as an engagement, the contact link is in the dashboard footer.
Installation
- Upload the plugin folder to
/wp-content/plugins/, OR install via the Plugins admin page. - Activate the plugin through the ‘Plugins’ menu in WordPress.
- Navigate to Tools → WP 7 Readiness to run the audit.
Frequently asked questions
Does this work before AND after WordPress 7.0 is installed?
Yes. On pre-7.0 sites it operates as a pre-flight audit. On post-7.0 sites it operates as a post-flight verification — checking that the upgrade landed cleanly.
Will it modify my site?
No. The plugin is strictly read-only. It scans your configuration and files; it does not write any changes.
How long does the audit take?
Typically under 5 seconds on most sites. The custom-code static scan is capped at 1500 files to ensure even very large sites complete quickly.
Does it cover everything in the 80-point manual checklist?
It covers the 30+ items that can be automated. The remaining 50 are human-judgment items — has the rollback been tested? has the AI Connectors policy been signed off? has the on-call rota been confirmed? — that no plugin can verify. The dashboard links to the printable checklist for the full audit.
Changelog
Initial release.
1.0.7
- Plugin review compliance. Managed-host detection no longer assumes a hardcoded server filesystem layout — Plesk is now detected from the
DOCUMENT_ROOT/SERVER_SOFTWAREenvironment signals and the control-panel install directory instead of matchingABSPATHagainst a fixed vhost path. No functional change: the same hosts are detected, and detection staysopen_basedir-safe. Contributors list corrected to the plugin’s WordPress.org account. The legacy-migration success notice now signals via a transient set by the nonce-verified migrate action instead of a URL parameter, resolving the Plugin Check nonce-verification warnings (and making the notice reliably display).
1.0.6
- WordPress.org submission readiness. All Plugin Check ERRORs and most WARNINGs resolved: short PHP tags converted, direct filesystem operations refactored to use WP_Filesystem, $_POST/$_SERVER inputs unslashed before sanitization, readme tags trimmed to 5, build script now excludes hidden files. No functional changes — same audit, same autofixes, same snapshot safety net. Ready for the WP.org plugin directory review.
1.0.5
- Distribution improvements. The self-hosted GitHub variant gained automated release delivery; the WordPress.org distribution uses WordPress.org’s native plugin-update channel.
1.0.4
- Fix: Plesk detection now works under
open_basedirrestrictions. v1.0.2’sis_dir(/usr/local/psa)check silently failed when the vhost’sopen_basedirexcluded/usr/local/psa/. New detection uses ABSPATH (/var/www/vhosts/...), DOCUMENT_ROOT, and SERVER_SOFTWARE signals — all open_basedir-safe. - Grading curve relief during major-release week. Within 14 days of a WordPress major release, plugins and themes still tested against the immediately-prior major (6.9 when current is 7.0) are downgraded from WARN to INFO and excluded from the score. Vendors typically catch up within this window; penalizing every site on day one was unfair. Auto-expires 14 days after the release date.
- Accept-as-known-risk override mechanism. Each warn/fail finding now has an “Accept as known risk” link. Click to acknowledge — the finding still appears in the report (with an “Accepted risk” tag) but is excluded from the readiness score calculation. Real enterprise audit pattern, fully reversible via “Un-accept” button.
1.0.3
- Fix: Re-run audit spinner appearing on page load and never stopping. The v1.0.1 spinner icon used the HTML
hiddenattribute to start hidden, but the plugin’s.wp7rc-btn__iconclass setdisplay: inline-blockwhich silently overrode[hidden]. The spin animation then ran constantly. Added an explicit[hidden]CSS override so the spinner stays hidden until the button is clicked.
1.0.2
- Fix: Custom-code scan no longer false-positives on common vendor plugins. The previous scope included Advanced Custom Fields, WPGraphQL, Two-Factor, page builders, and other widely-installed plugins that ship their own WordPress 7.0 compatibility updates. Flagging their internal code as if it were user-owned created noise. The vendor-skip list now covers 30+ common plugin slugs across page builders, SEO, ACF, GraphQL/headless, security, cache, forms, translation, and backup.
- Fix: Backup-plugin check now detects managed-host snapshot systems. Previously warned even on Plesk / WP Engine / Kinsta / Pantheon / Pressable / SiteGround / Flywheel / GoDaddy Managed WordPress / cPanel / DreamHost installs where host-level backups are the standard. The check now detects 10 managed-host platforms and reports PASS with “host-level snapshots assumed” instead.
Screenshots
For developers
Is this your plugin? Show off the numbers.
Add a live badge to your site, docs or GitHub README. It updates on its own — no account needed.
Best Champlin Pre-Flight Audit alternatives
All audit plugins →


FAQ
Champlin Pre-Flight Audit: quick answers
Straight answers, pulled from live WordPress.org data.
Live data from WordPress.org · checked Oct 14, 2026
Is Champlin Pre-Flight Audit free?
Yes. Champlin Pre-Flight Audit is free to download and use from the official WordPress.org plugin directory.
Is Champlin Pre-Flight Audit safe to use in 2026?
Champlin Pre-Flight Audit works, but test it on a staging site before relying on it in 2026. Was last updated 3 months ago, and scores 49/100 on our health check.
How many websites use Champlin Pre-Flight Audit?
Champlin Pre-Flight Audit is active on <10 WordPress websites and has been downloaded 196 times since it launched in July 2026. It was downloaded 63 times in the last 30 days.
Does Champlin Pre-Flight Audit work with WordPress 7.1?
Champlin Pre-Flight Audit is officially tested up to WordPress 7.0.7, while the latest release is 7.1.3. It may still work, but try it on a staging site first.
What PHP version does Champlin Pre-Flight Audit need?
Champlin Pre-Flight Audit requires PHP 7.4 or higher. Most hosts run PHP 8.x today, so it works on any modern WordPress hosting.
When was Champlin Pre-Flight Audit last updated?
The latest version, 1.0.7, was released on July 11, 2026 (3 months ago).
Who makes Champlin Pre-Flight Audit?
Champlin Pre-Flight Audit is developed and maintained by Kevin Champlin.
What are the best alternatives to Champlin Pre-Flight Audit?
The most popular alternatives to Champlin Pre-Flight Audit are Audit Trail (20K+ installs), MYAIO (400+ installs) and Sa11y, the accessibility qu… (300+ installs).
Powered by PageForge
Want thousands of pages that rank like these? Build them in an afternoon.
This directory runs on the same engine as PageForge. Turn any spreadsheet, CSV or API into thousands of fast, SEO-ready WordPress pages — with schema, internal links and AI-written copy baked in.
- CSV, Google Sheets & API data sources
- AI content, schema & internal links per page
- Works with Elementor, Gutenberg, Yoast & Rank Math
- Free on WordPress.org — no credit card