

Beplus Security Headers & Script Auditor
Enable common HTTP security headers, scan your site for external scripts/styles, and pick your own Content-Security-Policy rules.

Use with caution
Beplus Security Headers & Scrip… works, but test it on a staging site before relying on it in 2026. Was last updated 1 month ago, and scores 60/100 on our health check.
- Tested with the latest WordPress (7.1)
- Small user base (<10 active installs)
- Very few reviews so far
How does it stack up?
Side-by-side on installs, updates, ratings & support


Daily downloads
Download spikes usually follow a new release — each site that auto-updates counts as a download.
Rankings
Where Beplus Security Headers & S… stands todayWordPress.org search rankings
Live position in the plugin search, top 100| Keyword | Position |
|---|---|
| content security policy | >100 |
| csp | #65 |
| headers | >100 |
| http-headers | >100 |
| security | >100 |
About Beplus Security Headers & Script Auditor
From the official readme · v1.0.1Description
Beplus Security Headers & Script Auditor gives WordPress site owners three things in one screen:
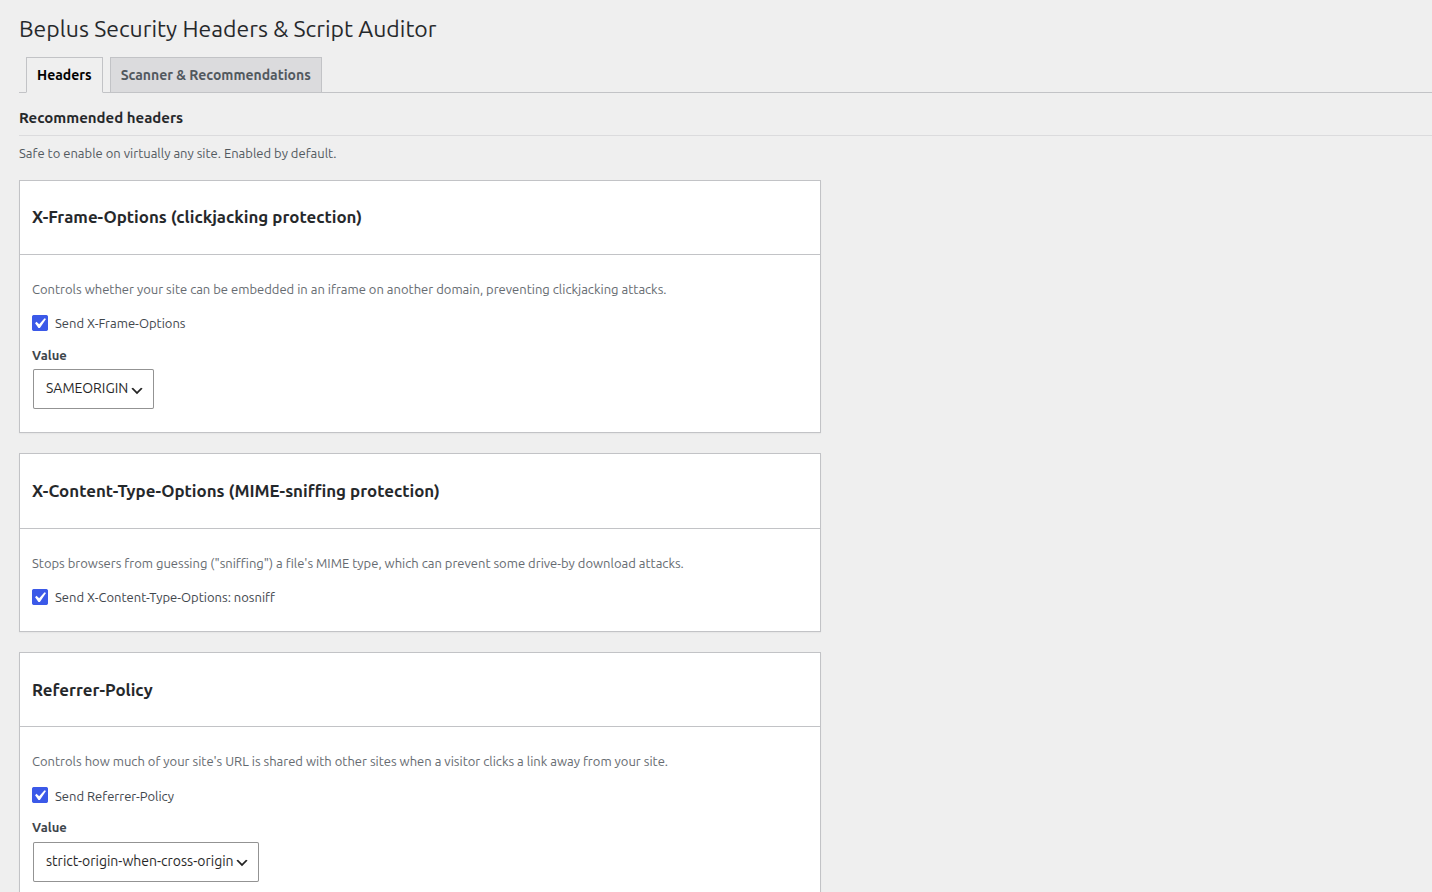
- Security header toggles — enable X-Frame-Options, X-Content-Type-Options, Referrer-Policy, Strict-Transport-Security, Permissions-Policy, Content-Security-Policy (with an optional report-only mode), and the legacy X-XSS-Protection header, each with sensible defaults.
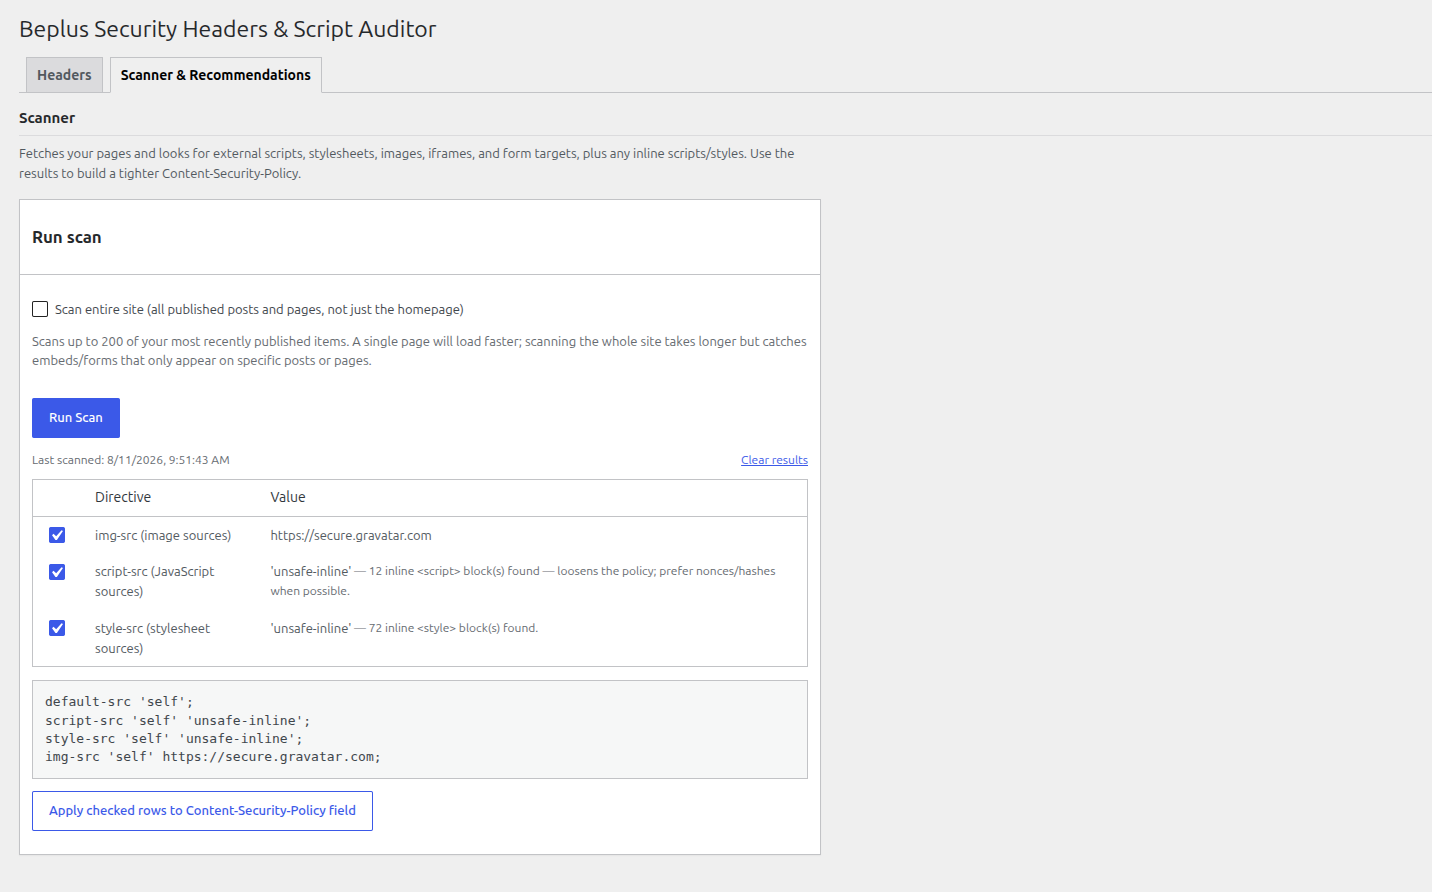
- A scanner — fetches your homepage, or optionally your whole site (up to 200 of your most recently published posts/pages), and lists every external script, stylesheet, image, iframe, and form target it finds, plus a count of inline scripts/styles.
- Recommendations you control — every finding is listed as a checkbox row; uncheck anything you don’t want, and the Content-Security-Policy preview updates live. Apply the checked rows to the CSP field with one click, review it, then press Save. Nothing is ever sent automatically.
There’s also a repeatable table for adding any other custom response header your site needs.
Why use this plugin
- No external service calls, tracking, or phone-home behaviour — the scan only requests pages on your own site.
- Every setting is sanitized on save, and header values are stripped of line breaks to prevent HTTP header injection.
- Sensible, conservative defaults: only X-Frame-Options, X-Content-Type-Options, and Referrer-Policy are enabled out of the box. HSTS, Permissions-Policy, CSP, and X-XSS-Protection are opt-in since they can affect how your site behaves and should be reviewed first.
Installation
- Upload the plugin files to the
/wp-content/plugins/beplus-security-headers-script-auditordirectory, or install the plugin through the WordPress plugins screen directly. - Activate the plugin through the ‘Plugins’ screen in WordPress.
- Go to the “Security Headers” menu item (in the main admin sidebar) to review the default header configuration.
- Open the Scanner tab and click “Run Scan” (optionally ticking “Scan entire site” first) to see what external resources your site loads, uncheck anything you don’t want, then apply the checked rows to the Content-Security-Policy field.
- Click “Save Changes” to apply your configuration.
Frequently asked questions
Will this break my site if I enable everything at once?
It can, especially Content-Security-Policy. Start with the scanner recommendations, use “Report-only mode” for CSP first to observe without blocking anything, and only switch to enforcing mode once you’ve confirmed the policy covers everything your site actually loads.
Does the scanner send my data anywhere?
No. It performs normal HTTP requests from your own server to pages on your own site, using the built-in WordPress HTTP API. Nothing is sent to any third party.
Does this replace a full security audit?
No. Even the whole-site option only scans your homepage plus your most recently published posts/pages (capped at 200) and is meant as a starting point for building a Content-Security-Policy, not a substitute for a complete security review of your site.
Changelog
Recommended update: fixes an invalid Permissions-Policy header sent with the plugin's own default settings, and a similar risk in manually-edited CSP values.
1.0.1
- Fix: The Permissions-Policy and Content-Security-Policy fields (“one directive per line”) joined lines with a plain space instead of the separator each header actually requires. Permissions-Policy needs a comma between directives — the plugin’s own default value (three directives, no commas) sent an invalid header out of the box whenever the feature was enabled. CSP needs a semicolon between directives; a manually-added line without a trailing
;merged into the previous directive.
1.0.0
- Initial release: security header toggles, homepage/whole-site scanner with a pick-and-choose CSP checklist, and custom header repeater.
Screenshots
For developers
Is this your plugin? Show off the numbers.
Add a live badge to your site, docs or GitHub README. It updates on its own — no account needed.
Best Beplus Security Headers & Scr… alternatives
All content security policy plugins →


FAQ
Beplus Security Headers & Script Au…: quick answers
Straight answers, pulled from live WordPress.org data.
Live data from WordPress.org · checked Oct 17, 2026
Is Beplus Security Headers & Scrip… free?
Yes. Beplus Security Headers & Scrip… is free to download and use from the official WordPress.org plugin directory.
Is Beplus Security Headers & Scrip… safe to use in 2026?
Beplus Security Headers & Scrip… works, but test it on a staging site before relying on it in 2026. Was last updated 1 month ago, and scores 60/100 on our health check.
How many websites use Beplus Security Headers & Scrip…?
Beplus Security Headers & Scrip… is active on <10 WordPress websites and has been downloaded 220 times since it launched in August 2026. It was downloaded 72 times in the last 30 days.
Does Beplus Security Headers & Scrip… work with WordPress 7.1?
Yes. The developer has tested Beplus Security Headers & Scrip… up to WordPress 7.1.3, the latest release. It requires WordPress 6.0 or newer.
What PHP version does Beplus Security Headers & Scrip… need?
Beplus Security Headers & Scrip… requires PHP 7.4 or higher. Most hosts run PHP 8.x today, so it works on any modern WordPress hosting.
When was Beplus Security Headers & Scrip… last updated?
The latest version, 1.0.1, was released on September 13, 2026 (1 month ago).
Who makes Beplus Security Headers & Scrip…?
Beplus Security Headers & Scrip… is developed and maintained by rimbeplus.
What are the best alternatives to Beplus Security Headers & Scrip…?
The most popular alternatives to Beplus Security Headers & Scrip… are Cookies and Content Securit… (10K+ installs), Content Security Policy Man… (2K+ installs) and HTTP Security Header (1K+ installs).
Powered by PageForge
Want thousands of pages that rank like these? Build them in an afternoon.
This directory runs on the same engine as PageForge. Turn any spreadsheet, CSV or API into thousands of fast, SEO-ready WordPress pages — with schema, internal links and AI-written copy baked in.
- CSV, Google Sheets & API data sources
- AI content, schema & internal links per page
- Works with Elementor, Gutenberg, Yoast & Rank Math
- Free on WordPress.org — no credit card