


Authyo Passwordless Login
WordPress login security with brute-force protection, IP manager, security logs, XML-RPC protection, REST API protection, and passwordless OTP login.

Solid choice
Authyo Passwordless Login is a solid plugin choice in 2026, with a few things worth checking first. It runs on 10+ sites and was last updated 4 days ago, and scores 66/100 on our health check.
- Actively developed — last update 4 days ago
- Tested with the latest WordPress (7.1)
- Small user base (10+ active installs)
- Very few reviews so far
How does it stack up?
Side-by-side on installs, updates, ratings & support


Daily downloads
Download spikes usually follow a new release — each site that auto-updates counts as a download.
Rankings
Where Authyo Passwordless Login stands todayWordPress.org search rankings
Live position in the plugin search, top 100| Keyword | Position |
|---|---|
| brute force protection | >100 |
| disable xmlrpc | #35 |
| login security | >100 |
| passwordless login | #35 |
| rest api security | >100 |
Version adoption
Share of active sites per release.
About Authyo Passwordless Login
From the official readme · v1.0.10Description
Authyo Passwordless Login is a WordPress login security plugin that protects your site with brute-force protection, IP blacklisting, security activity logs, XML-RPC blocking, REST API protection, and a custom login URL. All security features work immediately after activation — no API keys or account registration needed.
Optionally, add Authyo API credentials to enable passwordless OTP login where users log in with a one-time password sent to their email instead of a traditional password.
Security features that work without API keys:
- Brute-force protection — Limit login attempts per IP and username with progressive lockout durations. Repeat offenders are automatically blacklisted.
- IP Manager — Whitelist trusted IPs and blacklist attackers. Includes search, filter, pagination, and per-page selector for large lists.
- Security activity logs — Track every login, logout, failed attempt, lockout, and blocked access. Includes request URL tracking, date filters, search, and CSV export.
- Disable XML-RPC — Block xmlrpc.php requests at the server level using .htaccess rules. Removes X-Pingback headers and XML-RPC discovery links. Falls back to PHP blocking on Nginx.
- REST API Protection — Restrict access to WordPress REST API endpoints for unauthenticated users. Prevents data enumeration and unauthorized access while keeping essential endpoints functional.
- Custom login URL — Hide wp-login.php behind a custom URL slug to prevent automated attacks.
- Blocked IP logging — Every access attempt from blacklisted or locked-out IPs is logged with IP address, user agent, and request URL.
Passwordless login features (requires free Authyo API keys):
- Email OTP login — Users receive a one-time password via email and log in without a traditional password.
- Google Authenticator fallback — Server-side verified 2FA as a backup method after multiple OTP attempts.
- Secure login tokens — Cryptographically generated, single-use, browser-bound tokens that expire after 5 minutes.
- AJAX-powered login — Smooth login experience with no page reloads.
Video Tutorial
Learn how Authyo Passwordless Login works:
How It Works
Security (works immediately after activation):
- Activate the plugin — brute-force protection and security logs start automatically
- Go to Authyo Passwordless > Settings > Security tab
- Enable XML-RPC Protection, REST API Protection, and Custom Login URL as needed
- Visit Authyo Passwordless > Security Logs and IP Manager to monitor activity and manage IPs
Passwordless login (requires API keys):
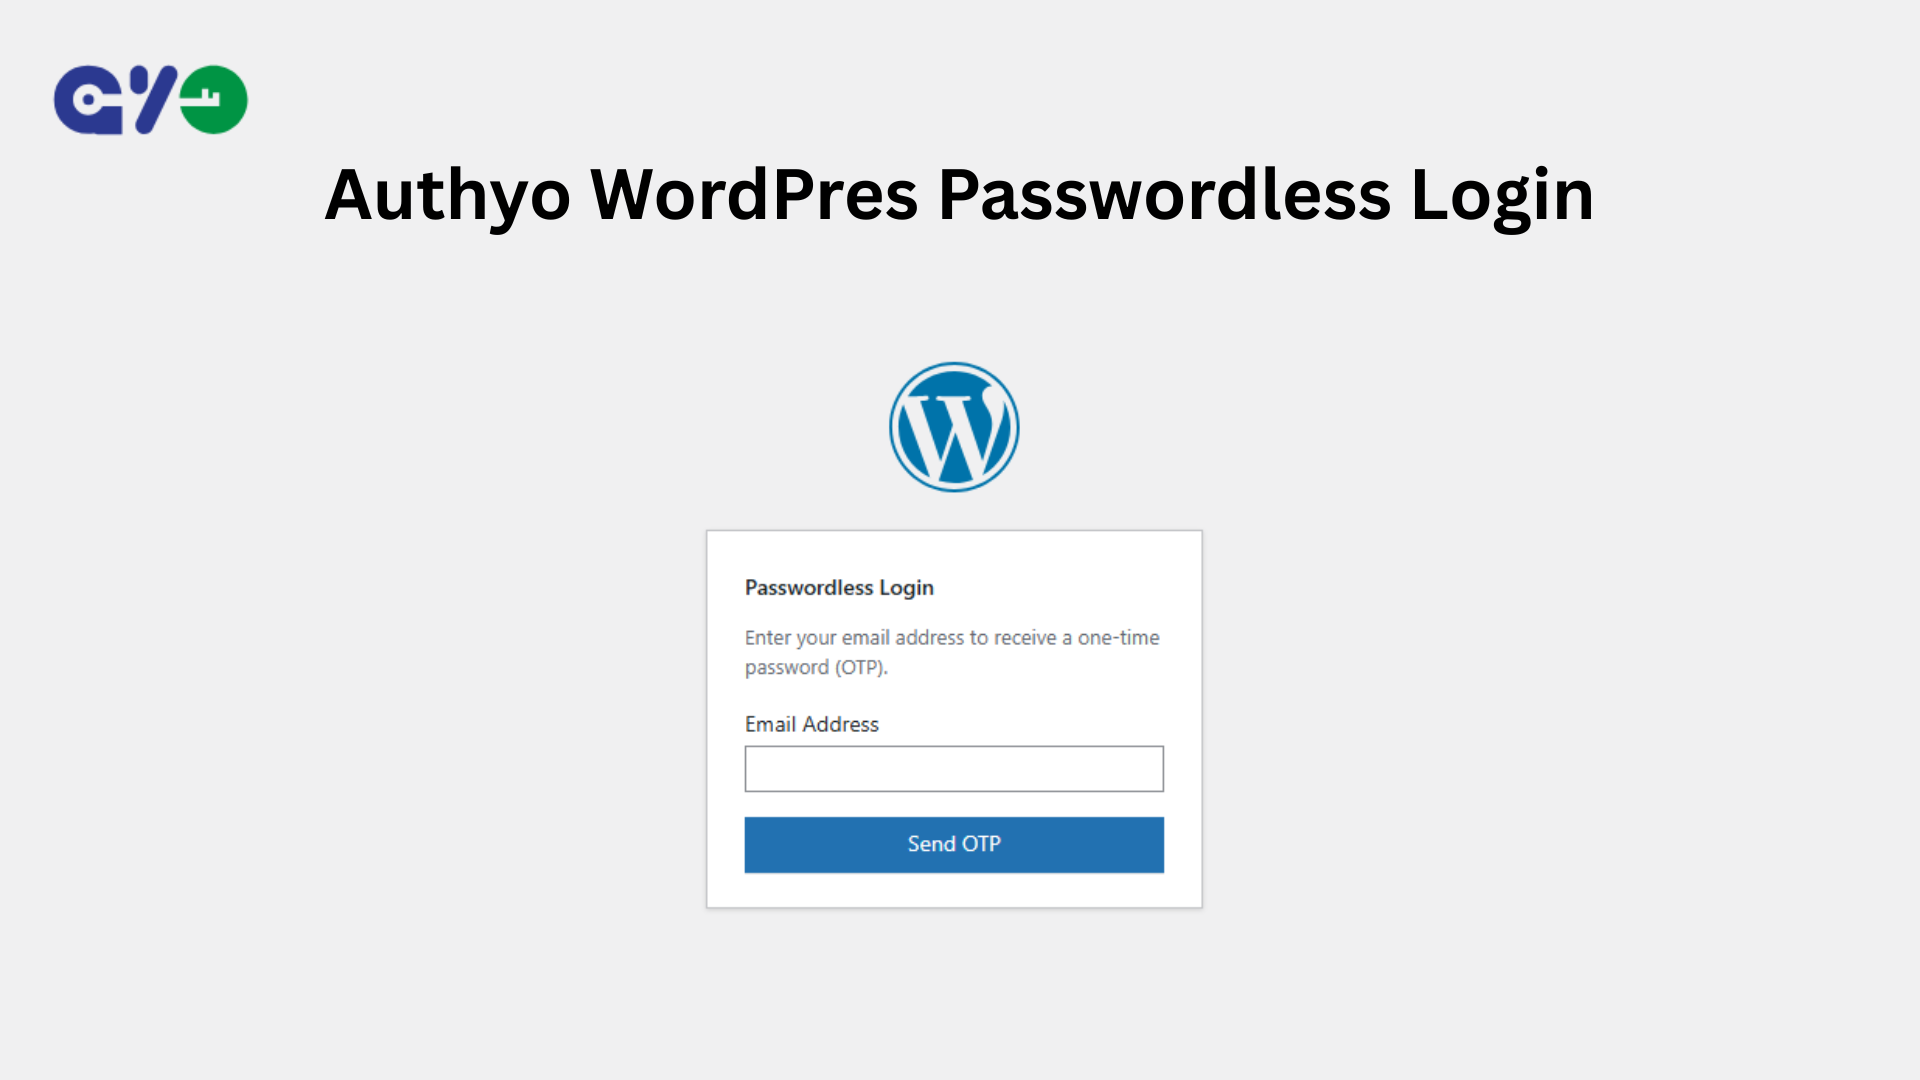
- User enters their email on the WordPress login page
- A one-time password (OTP) is sent to their email
- User enters the OTP code
- WordPress logs the user in automatically — no password required
External Services
This plugin connects to Authyo’s external API only for passwordless login and Google Authenticator features. All security features (brute-force protection, IP manager, security logs, XML-RPC protection, REST API protection, custom login URL) work locally without any external service.
OTP Authentication:
- User email address is sent to Authyo API when requesting an OTP
- OTP code and Mask ID are sent to Authyo API for verification
Google Authenticator Verification:
- During setup (Google Auth tab), the admin’s email address is sent from your server to the Authyo API to create the authenticator link and return a QR code
- The 6-digit authenticator code and the admin’s or user’s email address are sent from your server to the Authyo API for verification
- No Authyo script is loaded in the browser; all calls are made server-side
Usage Tracking (Opt-In Only):
If the user explicitly opts in, plugin version, WordPress version, and site URL are sent when settings are saved. Deactivation feedback is sent when the plugin is deactivated. No tracking data is sent without user consent.
Authentication Flow:
- After OTP verification, the plugin generates a secure single-use token using WordPress core functions
- Token is browser-bound using a hashed User-Agent signature to prevent session hijacking
- Token is stored temporarily in WordPress transients (5-minute expiry) and deleted immediately after use
Data Storage:
- OTP session data stored temporarily in WordPress transients (10-minute expiry)
- Login tokens stored temporarily in WordPress transients (5-minute expiry, single-use)
- Security logs stored in a custom database table with configurable retention
- IP whitelist and blacklist stored in a custom database table
- No user data is permanently stored beyond security logs
Service URLs:
Terms of Service: https://authyo.io/terms-service
Privacy Policy: https://authyo.io/privacy-policy
Installation
- Upload the
authyo-passwordless-loginfolder to/wp-content/plugins/ - Activate the plugin from the Plugins menu
- Security features start working immediately
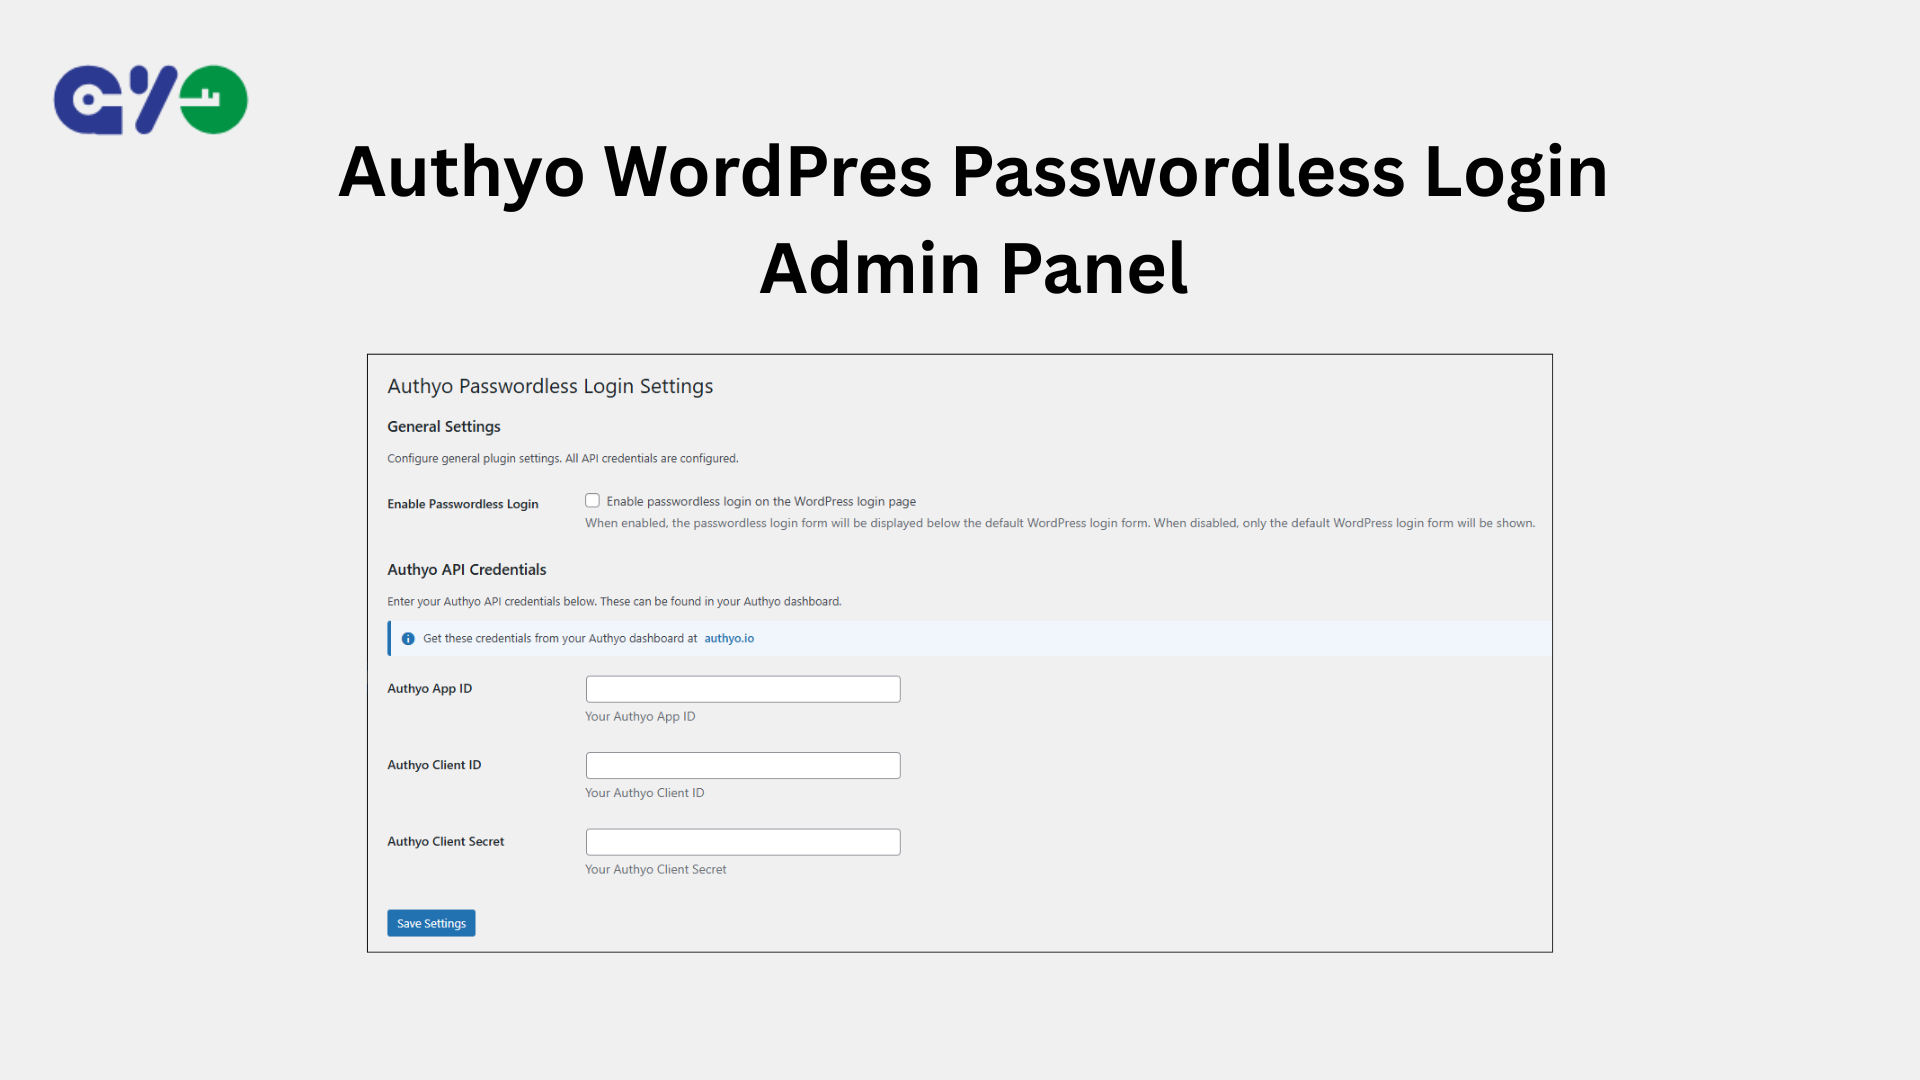
- For passwordless login: go to Authyo Passwordless > Settings and enter your Authyo API credentials from authyo.io
Frequently asked questions
Do I need API keys to use the security features?
No. Brute-force protection, IP manager, security logs, XML-RPC protection, REST API protection, and custom login URL all work without any API keys. You only need Authyo API keys for the passwordless OTP login feature.
How does brute-force protection work?
The plugin tracks failed login attempts per IP address and per username. After exceeding the configured threshold, the IP or username is temporarily locked out. Each subsequent lockout lasts longer (progressive durations). Repeat offenders can be automatically blacklisted permanently.
What does REST API Protection do?
It restricts access to WordPress REST API endpoints for unauthenticated users. By default, WordPress exposes REST API endpoints like /wp-json/wp/v2/users that can reveal usernames and other site data. When enabled, only logged-in users can access the REST API while essential public endpoints continue to work normally.
What does XML-RPC protection do?
It blocks all requests to xmlrpc.php at the server level using .htaccess rules on Apache and LiteSpeed servers. On Nginx servers, a PHP-level fallback handles the blocking. It also removes the X-Pingback header and XML-RPC discovery links. Whitelisted IPs are exempt.
How does passwordless login work?
Users enter their email address on the login page, receive a one-time password via email, enter the OTP code, and are logged in automatically. No password is needed. Requires Authyo API keys.
How do I manage blocked IPs?
Go to Authyo Passwordless > IP Manager. You can search by IP or label, filter, and paginate through whitelisted and blacklisted IPs. The page also shows active lockouts with options to unlock or permanently blacklist IPs.
I blocked my own IP and can’t reach the login page. What do I do?
Add define( 'AUTHYO_DISABLE_IP_BLOCKING', true ); to your wp-config.php file. This temporarily turns off all IP blacklisting and lockouts. Log in, remove your IP from Authyo Passwordless > IP Manager (or whitelist it), then delete the line from wp-config.php again.
My site is behind Cloudflare or a reverse proxy. Will lockouts work correctly?
By default the plugin uses the connecting IP address, which cannot be faked. Behind a proxy or CDN, that is the proxy’s address, so all visitors would share one IP. Use the authyo_passwordless_client_ip filter to return the real visitor IP from the header your proxy sets, for example CF-Connecting-IP on Cloudflare. Only do this if your server accepts traffic exclusively from that proxy, otherwise the header can be faked.
Are OTP and authenticator codes protected against guessing?
Yes. Each OTP or Google Authenticator session allows 5 attempts, each account allows 10 attempts per 15 minutes, and each account can request at most 5 OTP emails per 15 minutes. These limits apply even when brute-force protection is turned off.
Can I use this with custom login pages?
Yes. Use the shortcode [authyo_login] on any page, or call authyo_passwordless_login_form() in your theme templates.
Is this plugin secure?
Yes. The plugin implements multiple security layers including XML-RPC blocking at server level, REST API protection, brute-force protection with progressive lockouts, nonce verification for all AJAX requests, cryptographically secure token generation, browser-bound single-use tokens, server-side Google Authenticator verification, open redirect prevention, and blocked IP logging.
Changelog
Security hardening and a new Google Authenticator setup for administrators. Recommended for all users.
1.0.10
- New: Google Authenticator setup with live status, per-administrator setup and an overview of all administrators
- New: Google Authenticator login option shown only to accounts that have set it up
- Improved: Plugin settings moved to a top-level “Authyo Passwordless” admin menu
- Security hardening for OTP verification, login tokens and the custom login URL
- Bug fixes and performance improvements
1.0.9
- Performance improvements
1.0.8
- Performance improvements
1.0.7
- Performance improvements and stability enhancements
1.0.6
- Added REST API Protection to restrict unauthorized access to WordPress REST API endpoints
1.0.5
- Added XML-RPC protection with server-level .htaccess blocking and PHP fallback
- Added request URL tracking in security logs
- Added blocked IP logging for blacklisted and locked-out access attempts
- Added search and pagination to IP Manager with per-page selector (20, 50, 100)
- Added whitelist and blacklist count summary in IP Manager
- Added server-side verification for Google Authenticator
- Migrated IP whitelist/blacklist data from wp_options to a dedicated database table
- Improved login token security and validation
- Improved redirect security across login flows
- Fixed “page not found” issue with custom login URL after OTP verification
- Fixed database compatibility with MySQL strict mode
- Fixed database upgrade reliability on various server environments
- Multiple security hardening improvements
- General bug fixes and performance improvements
Screenshots
For developers
Is this your plugin? Show off the numbers.
Add a live badge to your site, docs or GitHub README. It updates on its own — no account needed.
Best Authyo Passwordless Login alternatives
All brute force protection plugins →

FAQ
Authyo Passwordless Login: quick answers
Straight answers, pulled from live WordPress.org data.
Live data from WordPress.org · checked Sep 29, 2026
Is Authyo Passwordless Login free?
Yes. Authyo Passwordless Login is free to download and use from the official WordPress.org plugin directory.
Is Authyo Passwordless Login safe to use in 2026?
Authyo Passwordless Login is a solid plugin choice in 2026, with a few things worth checking first. It runs on 10+ sites and was last updated 4 days ago, and scores 66/100 on our health check.
How many websites use Authyo Passwordless Login?
Authyo Passwordless Login is active on 10+ WordPress websites and has been downloaded 1,071 times since it launched in January 2026. It was downloaded 152 times in the last 30 days.
Does Authyo Passwordless Login work with WordPress 7.1?
Yes. The developer has tested Authyo Passwordless Login up to WordPress 7.1.2, the latest release. It requires WordPress 5.0 or newer.
What PHP version does Authyo Passwordless Login need?
Authyo Passwordless Login requires PHP 7.2 or higher. Most hosts run PHP 8.x today, so it works on any modern WordPress hosting.
When was Authyo Passwordless Login last updated?
The latest version, 1.0.10, was released on September 25, 2026 (4 days ago).
Who makes Authyo Passwordless Login?
Authyo Passwordless Login is developed and maintained by Konceptwise Digital Media Pvt Ltd.
What are the best alternatives to Authyo Passwordless Login?
The most popular alternatives to Authyo Passwordless Login are Kadence Security (700K+ installs), Titan Anti-spam & Security (50K+ installs) and Honeypot Toolkit (400+ installs).
Powered by PageForge
Want thousands of pages that rank like these? Build them in an afternoon.
This directory runs on the same engine as PageForge. Turn any spreadsheet, CSV or API into thousands of fast, SEO-ready WordPress pages — with schema, internal links and AI-written copy baked in.
- CSV, Google Sheets & API data sources
- AI content, schema & internal links per page
- Works with Elementor, Gutenberg, Yoast & Rank Math
- Free on WordPress.org — no credit card


