


Anti Session Hijacking
Stops session hijacking: signs a user out when their login session is used from a different IP address than the one it started on.

Use with caution
Anti Session Hijacking works, but test it on a staging site before relying on it in 2026. Was last updated 2 months ago, and scores 55/100 on our health check.
- Small user base (<10 active installs)
- Very few reviews so far
How does it stack up?
Side-by-side on installs, updates, ratings & support

Daily downloads
Download spikes usually follow a new release — each site that auto-updates counts as a download.
Rankings
Where Anti Session Hijacking stands todayWordPress.org search rankings
Live position in the plugin search, top 100| Keyword | Position |
|---|---|
| ip address | >100 |
| login security | >100 |
| session hijacking | #4 |
| Session security | >100 |
| user sessions | >100 |
About Anti Session Hijacking
From the official readme · v0.8.0Description
If someone steals a logged-in user’s session cookie, WordPress has no way of knowing. The cookie is valid, so the attacker is simply treated as that user — no password needed, and two-factor authentication never comes into play, because no new login ever happens.
Anti Session Hijacking closes that gap. It remembers the IP address each session was created from, checks it on every logged-in request, and immediately ends the session if the request comes from somewhere else. A stolen cookie stops working the moment it’s used from another machine.
How it works
WordPress core already records the IP address for every session token it issues at login. This plugin compares that recorded IP against the IP of each later request using the same session. On a mismatch it destroys that session token, clears the authentication cookie, and redirects the user to the login screen with an explanation. Other sessions belonging to the same user are left alone.
There is nothing to configure to get started — the check is active for every role as soon as you activate the plugin.
Features
- Verifies the client IP on every logged-in request against the IP recorded when the session was created.
- Immediately ends the hijacked session and signs the user out, without touching their other sessions.
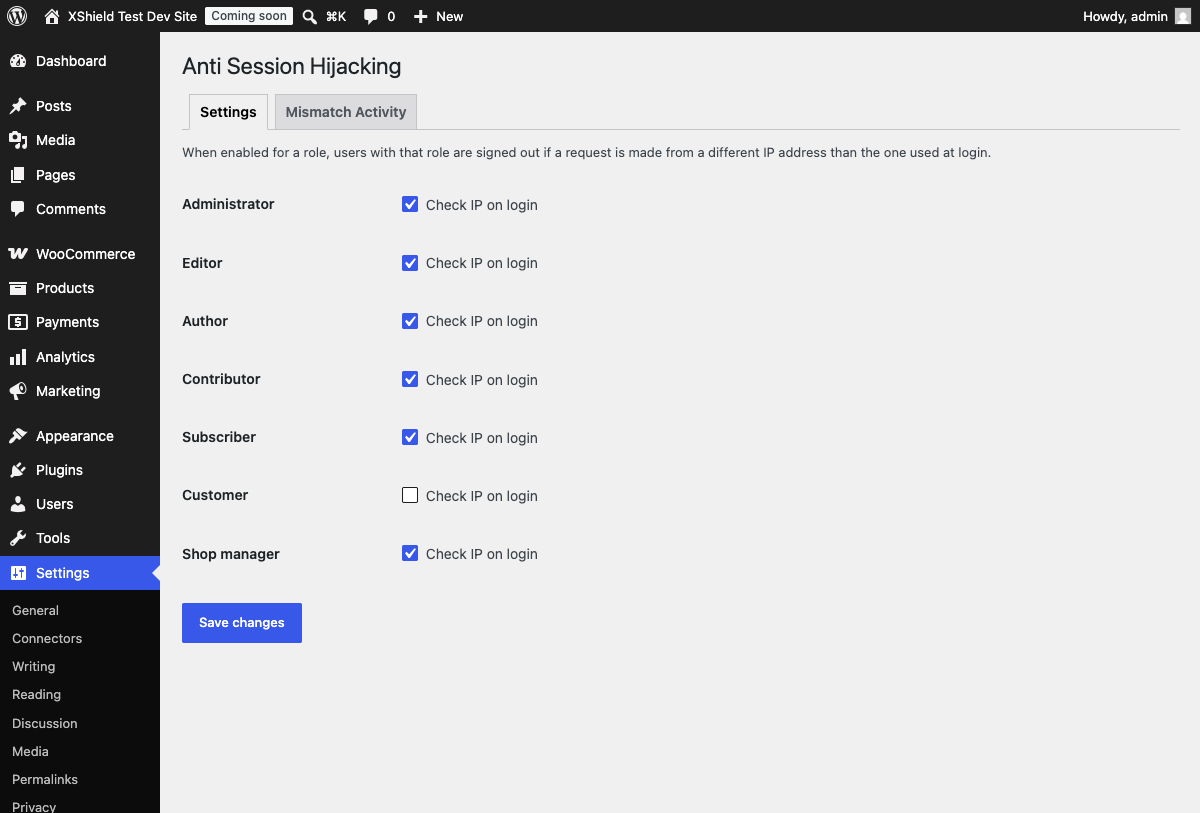
- Per-role control: enforce it for Administrators and Editors, relax it for roles that move between networks.
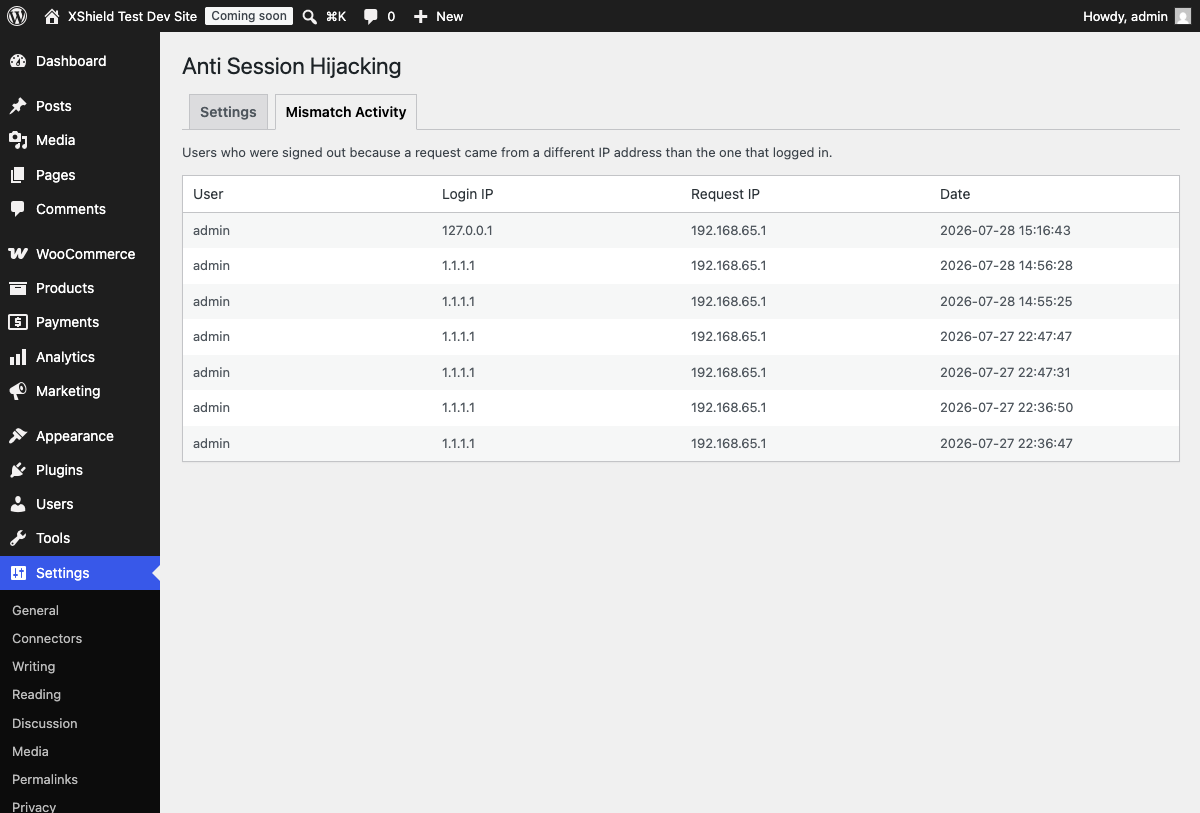
- Mismatch Activity log showing the user, the login IP, the IP that triggered the mismatch, whether it came from the same browser, and what kind of request ended the session — enough to tell a colleague switching on a VPN apart from something worth investigating.
- Correct client IP detection behind a reverse proxy, load balancer, or CDN such as Cloudflare, using X-Forwarded-For — trusted only when the connection genuinely originates from a known proxy, so the header cannot be spoofed to bypass the check.
- Runs entirely on your own server. No external requests, no third-party services, no accounts.
- Lightweight: one comparison per request, no dashboard nags, no upsells.
Who it’s for
This suits sites where an administrator or editor account being taken over would be expensive: membership sites, WooCommerce stores, client sites, multi-author publications, and any site where staff log in over the public internet.
It pairs well with two-factor authentication. 2FA protects the moment of logging in; this protects the session that exists afterwards.
What this plugin does not do
Being clear about the limits, so it’s the right fit:
- It does not block brute-force attacks or scan for malware — it only guards existing sessions.
- It does not stop an attacker who is on the same IP address as the victim.
- It cannot help if the site is served over plain HTTP, where cookies can be read in transit. Use HTTPS.
- Users whose IP address legitimately changes mid-session — some mobile networks, some corporate proxies, some VPNs — will be signed out and need to log in again. The per-role setting exists for exactly this reason.
Installation
- Upload the
anti-session-hijackingfolder to the/wp-content/plugins/directory, or install the plugin through the Add Plugins screen in WordPress. - Activate the plugin through the ‘Plugins’ screen in WordPress.
- That’s it — the check is immediately active for all roles. To adjust which roles it applies to, go to Settings → Anti Session Hijacking.
Frequently asked questions
Will this sign out users whose IP address changes for legitimate reasons?
Yes, and this is the main trade-off to be aware of. Some mobile carriers, corporate proxies, and VPNs rotate a user’s IP address mid-session, which is indistinguishable from a hijack as far as the check is concerned. If this is disruptive for a particular group of users, turn the check off for their role under Settings → Anti Session Hijacking. Administrator accounts are usually worth keeping strict.
Does it work behind Cloudflare, a load balancer, or a reverse proxy?
Yes. Behind a proxy, every request appears to come from the proxy’s own address, which would make the check useless. The plugin reads the real visitor IP from the X-Forwarded-For header instead — but only when the request genuinely arrives from a proxy address, so an attacker cannot simply send that header themselves to defeat the check. The trusted proxy ranges default to the usual private networks and can be adjusted with the antisehi_trusted_proxies filter.
Does it work with WooCommerce?
Yes. WooCommerce bundles Action Scheduler, which runs background jobs by having your site send an HTTP request to itself, carrying the logged-in user’s cookies. Those requests arrive from the server’s own address rather than the user’s, so the plugin deliberately does not check them — otherwise every administrator on a WooCommerce site would be signed out repeatedly. WordPress’s own Site Health tests work the same way and are covered by the same exemption. Requests from anywhere else are checked as strictly as ever, and the exempt addresses can be adjusted with the antisehi_self_addresses…
Does this replace two-factor authentication?
No, it complements it. Two-factor authentication protects the act of logging in. It does nothing once a session already exists, which is precisely when a stolen cookie is used. Running both covers the login and the session that follows.
Does this plugin send any data outside of my site?
No. Every check happens locally, using data WordPress already stores for the current session. There are no external requests, no telemetry, and no third-party services involved.
Does this plugin create any new database tables?
Yes, one: a mismatch log recording the username, the IP the session logged in with, the IP that triggered the mismatch, and a timestamp, each time a user is signed out by this plugin. It’s viewable under Settings → Anti Session Hijacking → Mismatch Activity. Nothing in it ever leaves your site, and the table — along with the plugin’s settings — is removed automatically when you uninstall the plugin.
Does it store personal data, and what about GDPR?
The mismatch log stores usernames and IP addresses, and IP addresses are considered personal data under the GDPR. They are stored only on your own server, only when a mismatch actually occurs, and are deleted entirely when you uninstall the plugin. If you keep a privacy policy listing what your site records, it’s worth mentioning this log.
Does this plugin update itself automatically?
Yes. When you activate it, it switches on WordPress’s own automatic updates for this plugin, so security fixes reach your site without waiting for someone to log in and press update. This is a security plugin, and an out-of-date one protects nobody. It uses the same setting as the Automatic Updates column on your Plugins screen, so nothing is hidden from you: the screen will show auto-updates as enabled, and you can switch them off there exactly like any other plugin. If you do switch them off, that choice sticks — deactivating and reactivating the plugin will not quietly turn them back on…
Will it sign out all of a user’s devices?
No. Only the specific session that failed the check is destroyed. If the same user is logged in on a phone and a laptop, ending the hijacked session leaves the other one signed in.
Changelog
0.8.0
- Fixed: on WooCommerce sites, administrators were repeatedly signed out while doing nothing unusual. WooCommerce bundles Action Scheduler, which starts background work by having the site send an HTTP request to itself and forwards the logged-in user’s cookies with it. That request arrives from the server’s own address, so a perfectly valid session looked like it had moved to a new machine. WordPress’s own Site Health loopback tests do the same thing.
- Requests a site makes to itself are no longer treated as hijacks. They are also no longer used to record a session’s address, which would have caused the opposite problem — the real user’s next request would then have looked like the intruder. Remote requests are checked exactly as strictly as before.
0.7.0
- Sessions ended during a background request — the admin heartbeat, an admin-ajax call, a REST call — now explain themselves. Previously the browser never followed the redirect, so the first thing you saw was WordPress’s own “Your session has expired” prompt, which gave no clue that this plugin was responsible. The login screen now states the real reason instead.
- The Mismatch Activity log records two new details: whether the request came from the same browser as the session it belongs to, and what kind of request ended it. A different address from the same browser is usually one person changing network or switching on a VPN, while a different address from a different browser is worth a closer look.
0.6.0
- Fixed: activating the plugin on a site behind a reverse proxy or CDN signed every logged-in user out and recorded a false entry in the Mismatch Activity log. Sessions created before activation carried the IP that WordPress core records (the proxy’s address), which the plugin then compared against the real visitor address it resolves itself — a guaranteed mismatch that was never an actual hijack.
- The plugin now records and compares its own IP value instead of reusing the one written by WordPress core, so the two can no longer disagree. A session first seen after upgrading is adopted at its current address and guarded from that point on, which means upgrading to this version does not sign anyone out either.
0.5.0
- Automatic updates for this plugin are now switched on when it is activated, so security fixes arrive without waiting for a manual update. It uses WordPress’s own per-plugin setting, stays visible in the Automatic Updates column on the Plugins screen, and can be turned off there at any time.
0.4.0
- Added translations for Dutch, German, French, and Spanish.
- Added a translation template (.pot) so the plugin can be translated into further languages.
0.3.0
- Renamed all internal classes, functions, options, and hooks to a unique
ANTISEHIprefix to avoid any chance of collisions with other plugins.
Screenshots
For developers
Is this your plugin? Show off the numbers.
Add a live badge to your site, docs or GitHub README. It updates on its own — no account needed.
Best Anti Session Hijacking alternatives
All ip address plugins →



FAQ
Anti Session Hijacking: quick answers
Straight answers, pulled from live WordPress.org data.
Live data from WordPress.org · checked Sep 29, 2026
Is Anti Session Hijacking free?
Yes. Anti Session Hijacking is free to download and use from the official WordPress.org plugin directory.
Is Anti Session Hijacking safe to use in 2026?
Anti Session Hijacking works, but test it on a staging site before relying on it in 2026. Was last updated 2 months ago, and scores 55/100 on our health check.
How many websites use Anti Session Hijacking?
Anti Session Hijacking is active on <10 WordPress websites and has been downloaded 252 times since it launched in August 2026. It was downloaded 67 times in the last 30 days.
Does Anti Session Hijacking work with WordPress 7.1?
Anti Session Hijacking is officially tested up to WordPress 7.0.6, while the latest release is 7.1.2. It may still work, but try it on a staging site first.
What PHP version does Anti Session Hijacking need?
Anti Session Hijacking requires PHP 7.4 or higher. Most hosts run PHP 8.x today, so it works on any modern WordPress hosting.
When was Anti Session Hijacking last updated?
The latest version, 0.8.0, was released on August 4, 2026 (2 months ago).
Who makes Anti Session Hijacking?
Anti Session Hijacking is developed and maintained by Martin van Wilderen.
What are the best alternatives to Anti Session Hijacking?
The most popular alternatives to Anti Session Hijacking are IP2Location Country Blocker (30K+ installs), User IP and Location (3K+ installs) and Show IP address (1K+ installs).
Powered by PageForge
Want thousands of pages that rank like these? Build them in an afternoon.
This directory runs on the same engine as PageForge. Turn any spreadsheet, CSV or API into thousands of fast, SEO-ready WordPress pages — with schema, internal links and AI-written copy baked in.
- CSV, Google Sheets & API data sources
- AI content, schema & internal links per page
- Works with Elementor, Gutenberg, Yoast & Rank Math
- Free on WordPress.org — no credit card


