

Security Plugin, Firewall & Malware Scanner with Auto Removal
Protect WordPress from malware, hackers, brute-force attacks & suspicious traffic. Includes firewall, login security, 2FA & vulnerability checks.

Escolha segura
Yes — Security Plugin, Firewall & Mal… is a safe, well-maintained plugin to use in 2026. It runs on 40K+ sites, is rated 4.8/5 and was last updated 2 weeks ago, and scores 94/100 on our health check.
- Comprovado em escala em mais de 40 mil sites ativos
- Loved by users — 4.8/5 from 398 reviews
- Desenvolvido ativamente — última atualização 2 semanas atrás
- Testado com as últimas WordPress (7.1)
- Responsive support — 97% of recent threads resolved
Como ele se acumula?
Lado a lado em instalações, atualizações, avaliações e suporte


Downloads diários
Os picos de download geralmente seguem uma nova versão — cada site que atualiza automaticamente é um download.
Rankings
Where Security Plugin, Firewall &… stands todayWordPress.org Classificações de pesquisa
Posição ao vivo na pesquisa de plugins, top 100| Palavra chave | Posição |
|---|---|
| 2FA | #7 |
| firewall | #3 |
| login | #50 |
| malware | #2 |
| segurança | #4 |
Adoção da versão
Compartilhamento de sites ativos por lançamento.
Divisão de classificação
★★★★★★★★★★ 4.8 from 398 reviews
About Security Plugin, Firewall & Malware Sca…
From the official readme · v2.192Descrição
Brute force, Login security & Two Factor Auth (2FA). Limit login. Malware & Vulnerabilities scan. FireWall. Enterprise ready security plugin.
SECURITY PLUGIN BY CLEANTALK (SPBCT)
We focus on eliminating the most common security threats for WordPress. At the same time, we strive to ensure that site performance remains unaffected. To achieve this, each release goes through automated and expert-driven testing pipelines. We also verify performance using Google PageSpeed Insights and GTMetrix. Typically, we release a new version twice a month to keep features up to date and protection strong.
SECURITY FEATURES
- Limit Login Attempts and rate limits for logins.
- Two Factor Authentication (2FA)
- Custom wp-login URL (wp-login.php)
- Hide Login Default Login Page
- Disable or Stop User Enumeration
- Brute force protection for WordPress accounts and passwords
- Security Protection for WordPress login form
- Security FireWall by IP, Networks, or Countries
- Web Application Firewall (WAF)
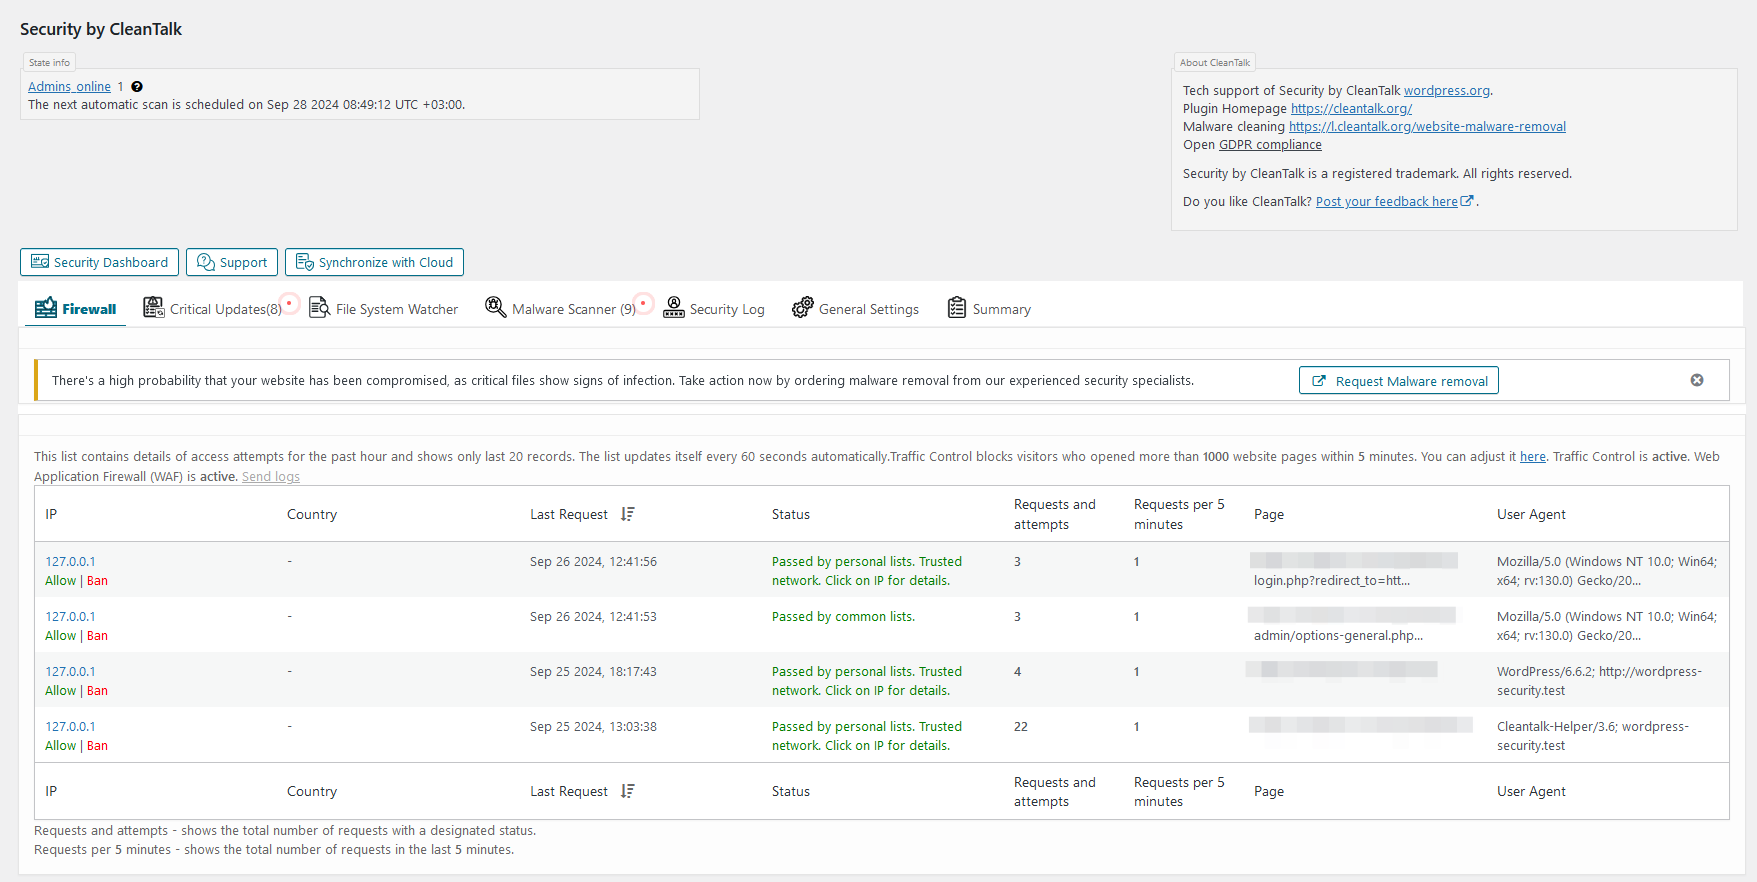
- Real-time traffic monitor (Visitors per pages, IPs, Countires and hits counts per page)
- Malware scanner with auto-cure function
- Daily auto malware scan
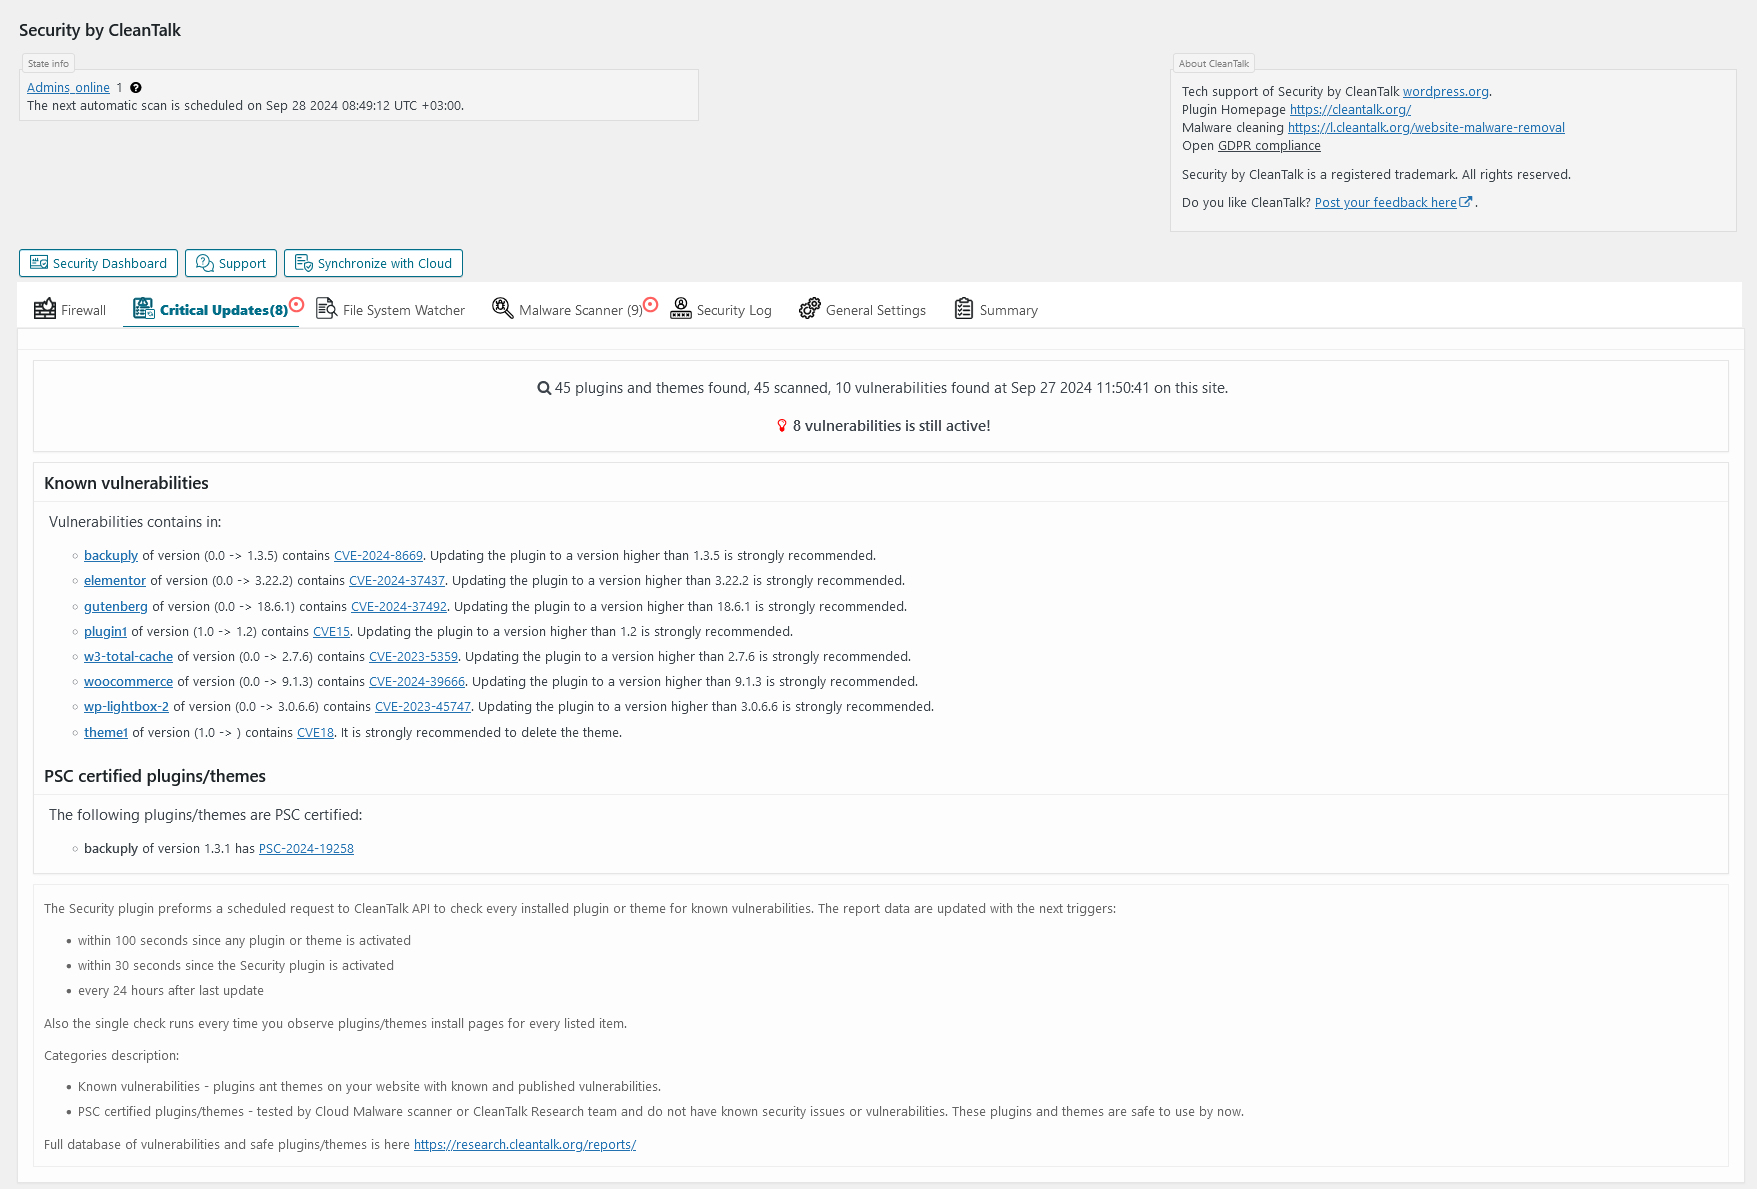
- Vulnerabilities scanner among installed plugins and themes
- Security weekly reports to email
- Notifications of login events to your website
FREE TRIAL THEN $9 PER YEAR
CleanTalk is a Cloud security service that protects your website from online threats and provides you great security instruments to control your website security. We provide detailed security stats for all of our security features to have a full control of security.
We believe the most honest approach is when every user pays a small fee for using the service, rather than relying on a freemium model where some users subsidize others. The fee is as low as price of a good cup of coffee! So, the security plugin does not have a PRO version-it is completely free and works in combination with our premium Cloud security service at cleantalk.org. Every user has full access to all features of both the service and the plugin. Also, please take a note about WordPress.org policy
BRUTE FORCE PROTECTION
Our default anti–brute-force policy works as follows,
- For any failed login attempt to the WordPress admin area, the plugin introduces a brief delay of a few seconds.
- The plugin reviews the security audit log every hour. If any IP address records 10 or more login attempts in that period, it will be blocked for 24 hours.
ALL BRUTE FORCE PROTECTION FUNCTIONS
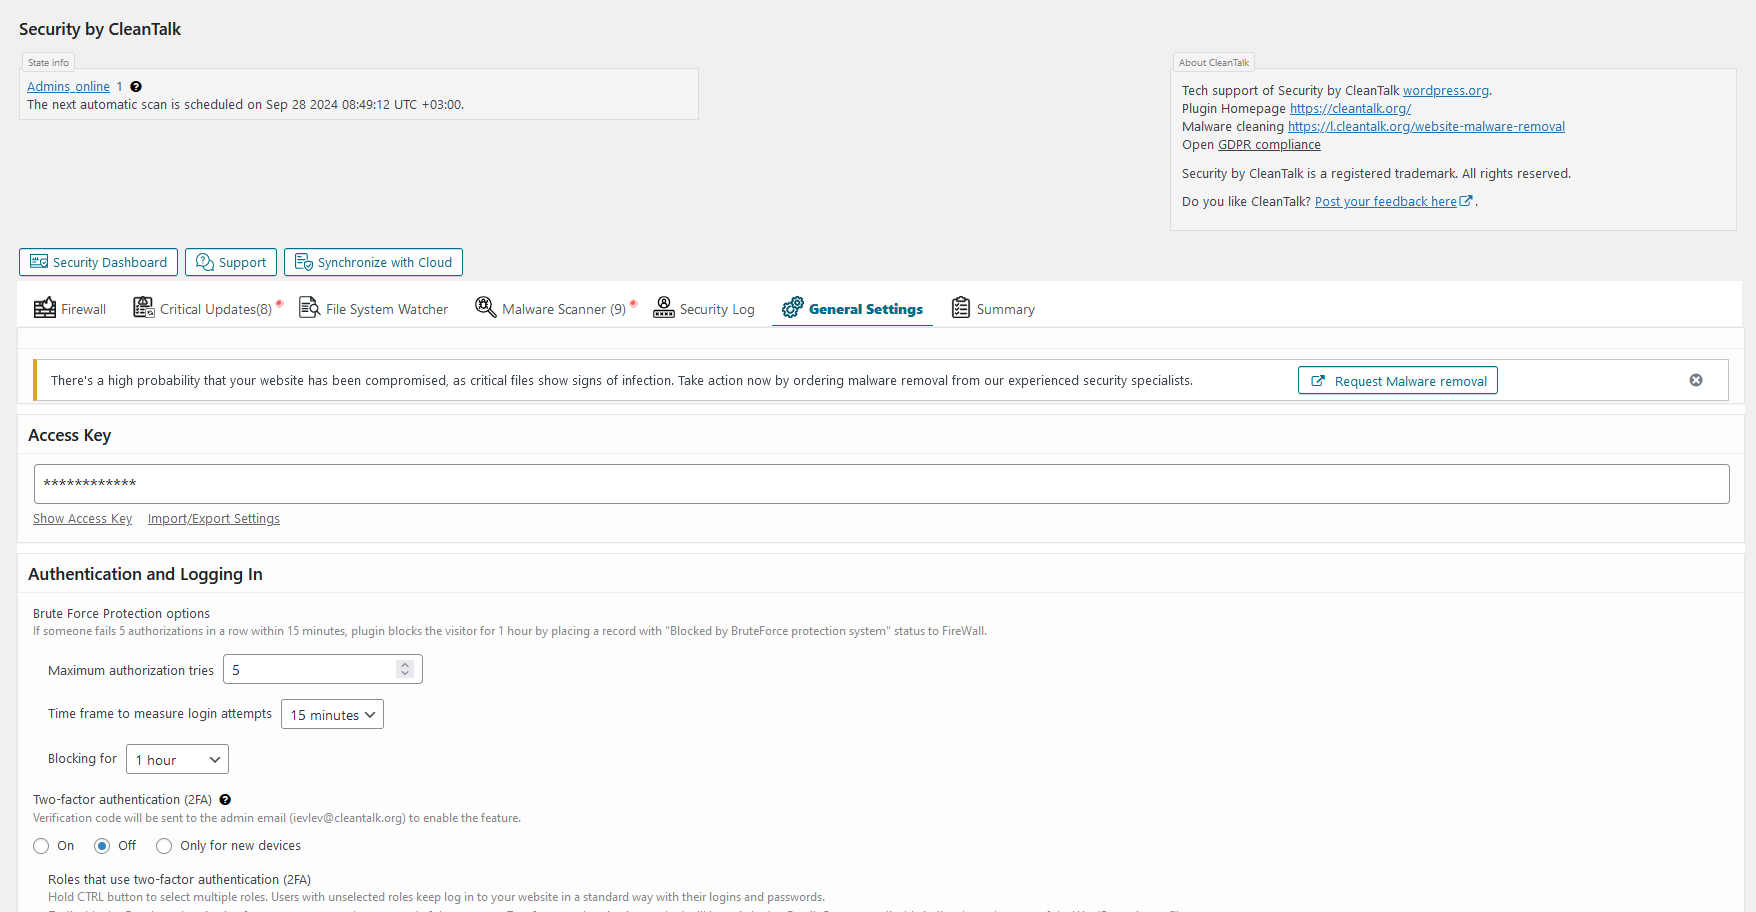
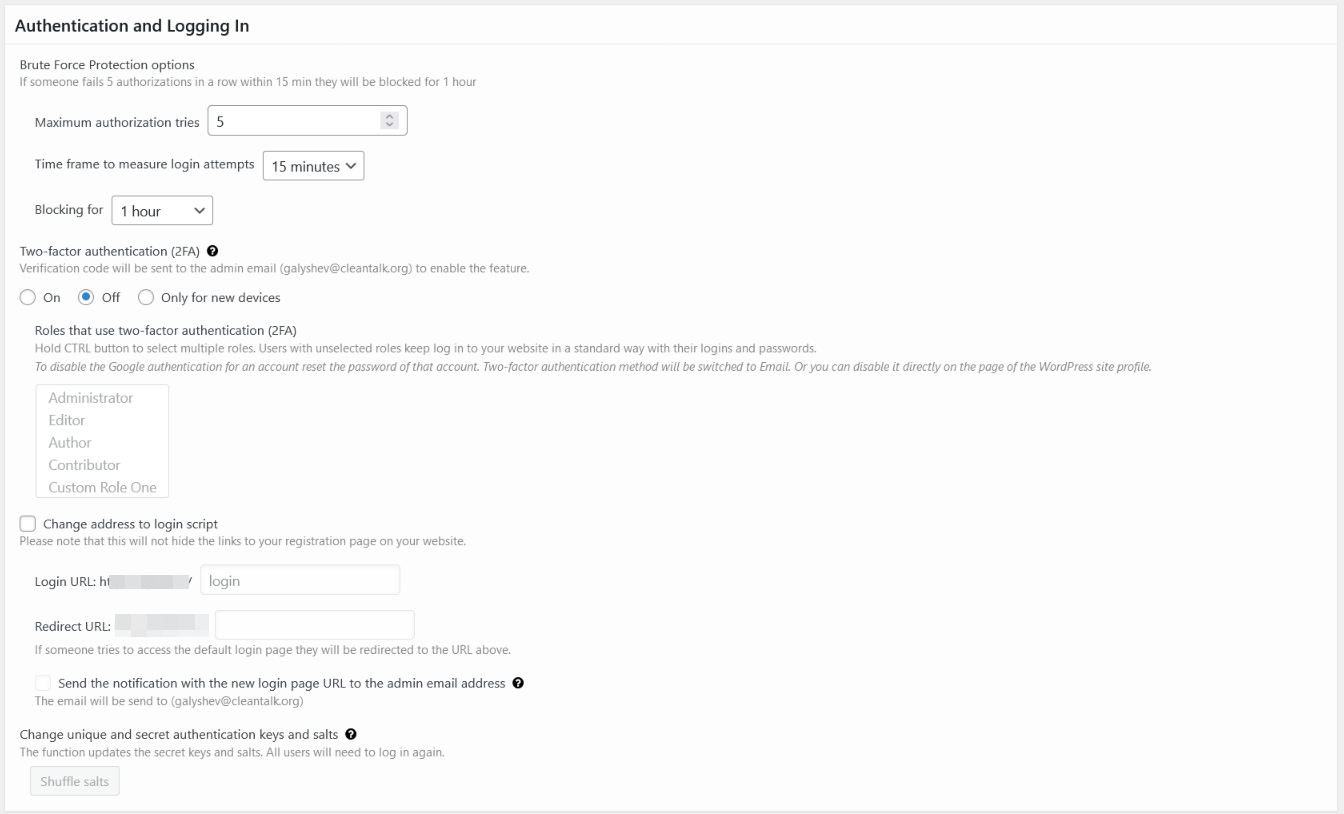
- Maximum failed attemtps to login before ban (default is 5). A failed attempt happens when either the login or password is incorrect.
- Time frame to count login attempts (default is 15 minutes).
- Ban to login time frame from 2 minutes to 24 hours (default is 1 hour).
- Two-factor authentication (2FA) with abillity to apply policy to specific users roles.
- Prevent collecting of login on password reset error. The option exclude the info about the login existing on password change error. Error message will be replaced with followed text: “If the user with the specified credentials exists, check your email for the password reset confirmation link. Then visit login page.”
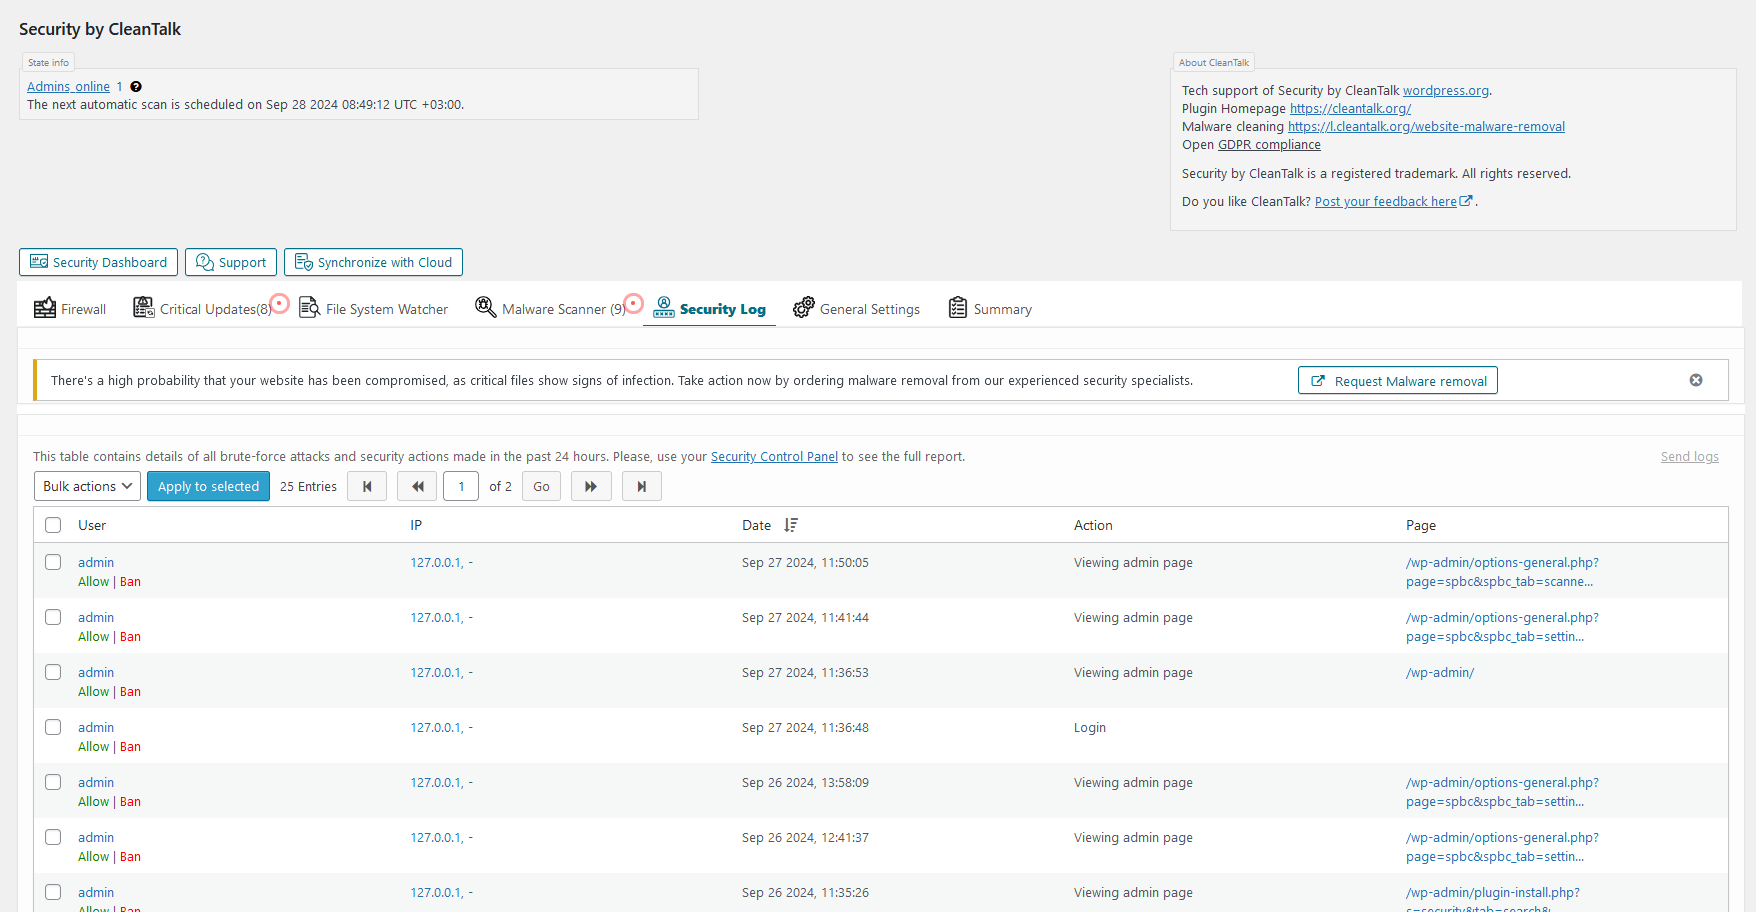
- Security Audit Log. Keeps track of actions in the WP Dashboard to let you know what is happening on your blog. With the Security Audit Log is very easy to see user activity in order to understand what changes have done and who made them. Security Audit Log shows who logged in and when and how much time they spent on each page.
- Two Factor Authentication (2FA). It requires a bit of your time but Two Factor (2 Step) Authentication immediately gives a much higher level of security.With your first authorization, the CleanTalk Security plugin remembers your browser and you won’t have to input your authorization code every time anymore. However, if you started to use a new device or a new browser then you are required to input your security authorization code. CleanTalk security plugin will remember your browser for 30 days.
- Change the URL of the wp-login page. This option helps you change the default wp-login URL (wp-login.php). Hackers use scripts for massive brute-force attacks, and since most sites use a default login page URL, hackers configure scripts for such URLs. When you change the URL of the authorization page, hackers will not have the opportunity to perform brute-force attacks in scripts in automatic mode. This option does not change files and does not rewrite URLs in system files. To return the address of the default authorization page, it is enough to disable the option in the plugin settings or set a new value. If you are using caching plugins, then you need to add a new authorization page in the caching exceptions.
- Leaked password check. This feature enhances your website’s security by continuously monitoring users’ passwords for potential exposure in known data breaches and on the dark web. It works in the background and requires no action from users unless a leak is detected.
SECURITY FIREWALL
To enhance the security of your site, you can use the CleanTalk Security FireWall, which will allow you to block access by HTTP/HTTPS to your website for individual IP addresses, IP networks and block access to users from specific countries. Use personal BlackList to block IP addresses with a suspicious activity to enhance the WordPress security.
Security FireWall may significantly reduce the risk of hacking and reduces the load on your web server. CleanTalk Security is fully compatible with the most popular VPN services. Also, CleanTalk security supports all search engines Google, Bing, Yahoo, Baidu, MSN, Yandex, and etc.
LIST OF FIREWALL FUNCTIONS
- Blocks or bypass visitors by IP, IP Network. Country blocking. It also has option to avoid blocking hits from major search engines like Google, Bing, Yahoo, Baidu, Yandex, and etc.
- Traffic control. CleanTalk security Traffic Control will track every single visitor no matter if they are using JavaScript or not and provides many valuable traffic parameters. Another option in Security Traffic Control – “Block user after requests amounts more than” – blocks access to the site for any IP that has exceeded the number of HTTP requests per hour. If this number of requests will be exceeded, this IP will be added to the Security FireWall Black List for 24 hours. Security Firewall has a limit for requests to your website (by default 1000 requests per hour, so you can change it) and if any IP exceed this threshold it will be added to security firewall for next 24 hours. It allows you to break some of the DDoS attacks.
- Limit Login Attempts. Limit Login Attempts – is a part of brute-force protection and security firewall.
- Web Application FireWall (WAF) for WordPress Security Plugin. The main purpose of Web Application FireWall (WAF) is real-time protection from unauthorized access, even if there are critical known/unknown vulnerabilities. Security Web Application FireWall catches all requests to your website and checks HTTP parameters that include,
- SQL Injection,
- Cross Site Scripting (XSS),
- uploading files from non-authorised users,
- PHP constructions/code,
- the presence of malicious code in the downloaded files.
In addition to effective information security and information security applications are required to know what is quality of protection and CleanTalk Security has logged all blocked requests that allow you to know and analyze accurate information. - You can see your Cleantalk Security Logs in your Dashboard CleanTalk’s research team updates WAF database each time as we find a vulnerability, it means plugin’s users get protection even against unpublished vulnurebilites.
- Learn more how to set up and test About Security Web Application Firewall
- Email Notifications when administrators or users are logged in. We added this option to our security plugin. Now you can receive notifications if you want to know about an unauthorized entrance to your WP Dashboard. Notification will be sent only when a user was able to authorize entering login and password. If you are logged into the admin panel from the saved session, then the alert won’t be sent.
MALWARE SCANNER WITH AUTO-CURE FUNCTION
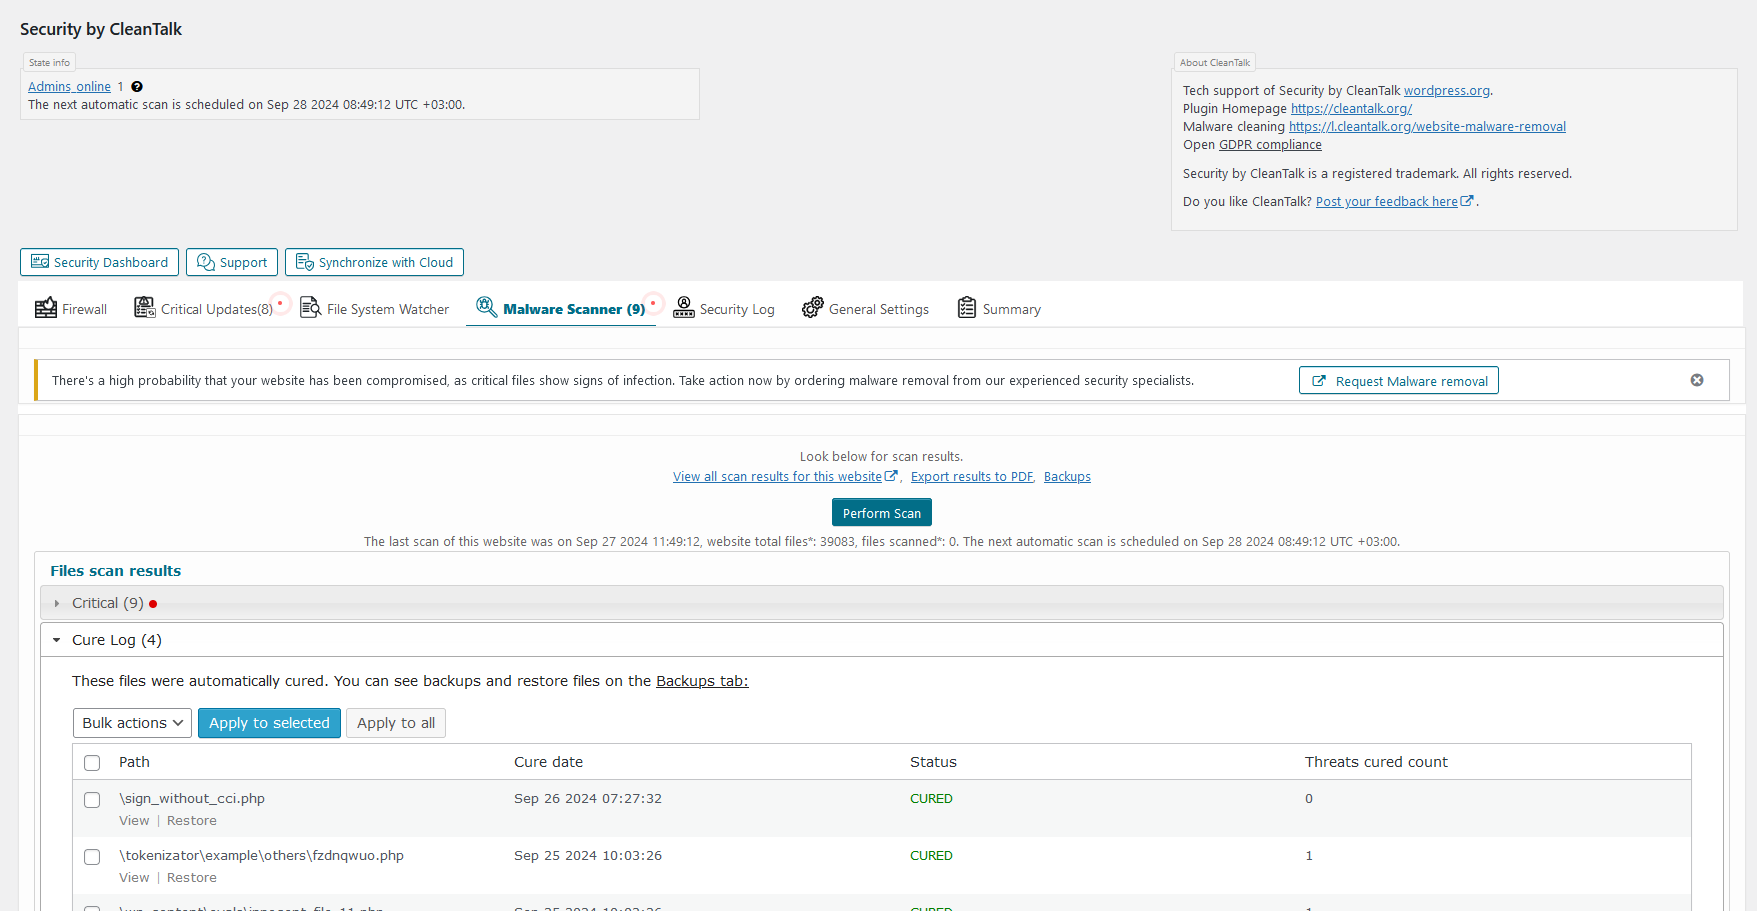
Scans WordPress files for hacker files or code for hacker code. Performs antivirus functions. Security Malware Scanner runs manually by users requests or automaticaly by WordPress cron. All of the results will send in your Security CleanTalk Dashboard with the details and you will be able to investigate them and see if that was a legitimate change or some bad code was injected.
If you are unsure how to identify, remove, or clean malware using the plugin, you can book a malware removal service with our Security & Pentest team.
As an alternative, you can use the Website Malware Scanner for frontend security and malware checks. It scans by URL and requires no plugins.
LIST OF MALWARE SCANNER, ANTIVIRUS FUNCTIONS
- Malware autoscanning. Scans the website automatically at intervals ranging from once every 12 hours to once every 30 days.
- Cure malware. It cures infected files automatically if the scanner knows cure methods for these specific cases. If the option is disabled then when the scanning process ends you will be presented with several actions you can do to the found files,
- Cure. Malicious code will be removed from the file.
- Replace. The file will be replaced with the original file.
- Delete. The file will be put in quarantine. Do nothing.
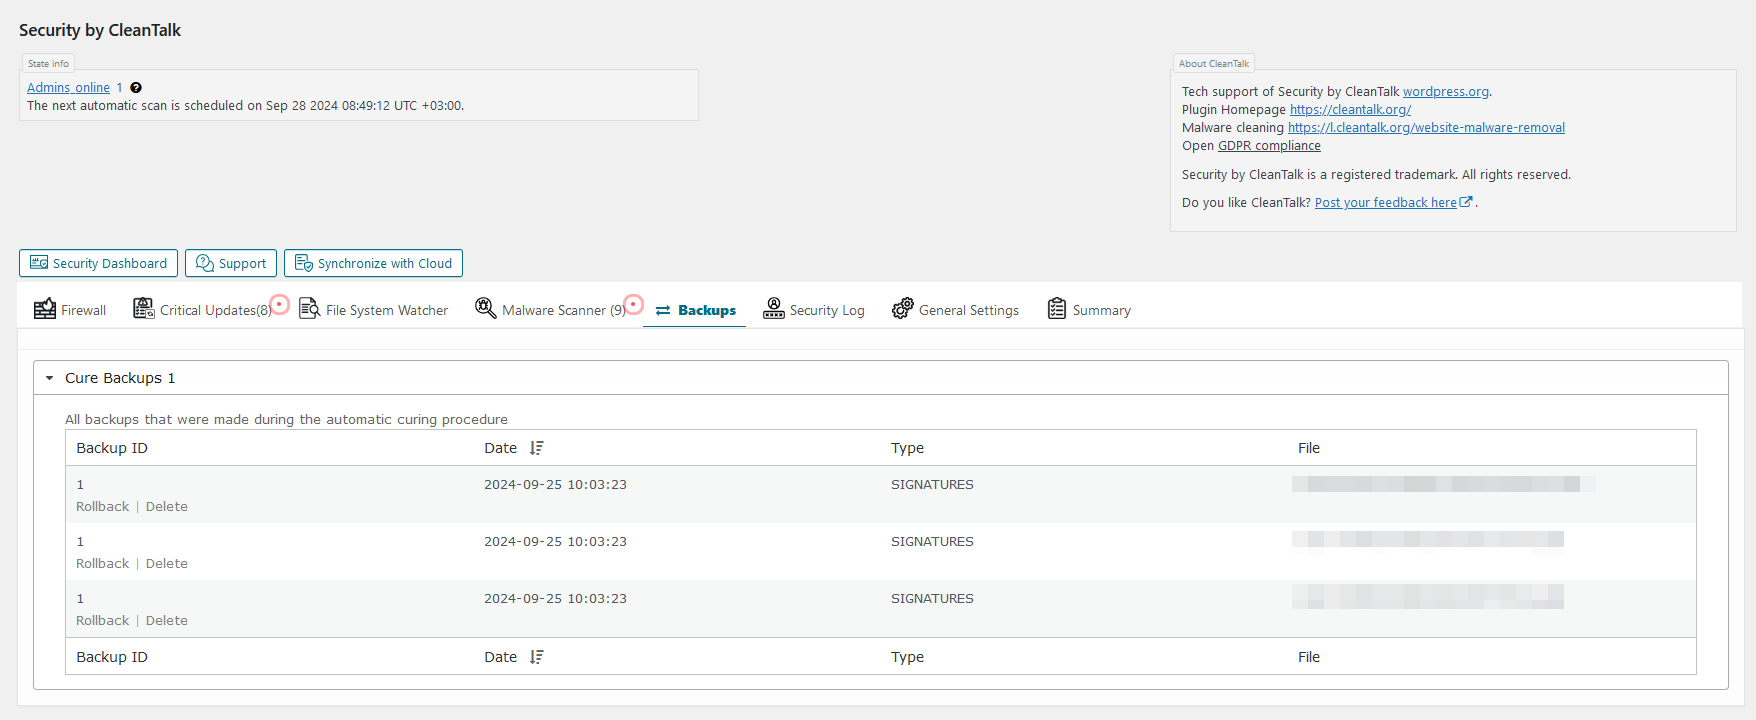
Before any action is chosen, backups of the files will be created and if the cure is unsuccessful it’s possible to restore each file.
- Security Malware Heuristic Check. This option allows you to check files of plugins and themes with heuristic analysis. Probably it will find more than you expect.
- Security Malware scanner to find SQL Injections. The CleanTalk Security Malware Scanner allows you to find code that allows performing SQL injection. It is this problem that the scanner solves.
- Operating system cron tasks analysis. This functional provides an overview of scheduled cron jobs on server that perform automated tasks.
- DB Trigger analysis. Will search for known malicious signatures in database triggers.
- List unknown files. Shows the list of found unknown files in the malware scanner report. Unknown files do not have known virus signatures and do not have suspicious code. Meanwhile, unknown files do not belong to the public plugins and themes at wordpress.org.
- File System Watcher. File system Watcher monitors changes in the file system. This allows to quickly respond to a site infection by tracking which files were affected. The Watcher makes file system snapshots as often as one hour and show difference up to seven days time frame.
- Feedback System. If you don’t have programming experience and don’t know, is there security issue or not, you send some files to CleanTalk Cloud and we check them for malware code. After checking we send you an email notification with results, is there viruses or not. Please, look at our guide How malware file analysis works About Scanner Feedback System
LIST OF THE MOST ACTIVE MALWARES BY FILENAMES
- radio.php
- admin-ajax.php
- .1235512.css
- 8sjdakSJ3.php
- wso.php
- cmd.php
- shell.php
- reverse_shell.php
- admin.php
The list is actual on July 15th, 2025. The latest data is the article Is my site infected?
VULNERABILITIES SCANNER AMONG INSTALLED PLUGINS AND THEMES
Plugin checks installed plugins and themes for known (published) vulnerabilities. If finds vulnerable plugin/theme, it sends an Email notification and shows data in the Critical updates tab.
List of the most recent vulnerabilities found and published by CleanTalk Research team,
- CVE-2025-5921 – SureForms – Unauthenticated XSS – POC, 200k+ installs.
- CVE-2025-3582 – Newsletter – Stored XSS to JS Backdoor Creation – POC, 300k+ installs.
- CVE-2025-2560 – Ninja Forms – Stored XSS to JS Backdoor Creation – POC, 700k+ installs.
The list is effective on July 18th, 2025. Updates are avaible on https://research.cleantalk.org/.
MISCELLANEOUS SECURITY OPTIONS
- Send additional HTTP headers option. There are several additional http-headers which added to the every http-requests by the plugin if this option is enabled:
- “X-Content-Type-Options” improves the security of your site (and your users) against some types of drive-by-downloads.
- “X-XSS-Protection” header improves the security of your site against some types of XSS (cross-site scripting) attacks.
- “Strict-Transport-Security” response header (often abbreviated as HSTS) informs browsers that the site should only be accessed using HTTPS, and that any future attempts to access it using HTTP should automatically be converted to HTTPS.
- “Referrer-Policy” make the
Refererhttp-header transferring more strictly.
- Collect and send PHP logs. Collect and send PHP error logs to your CleanTalk Dashboard where you can list them.
- Prevent collecting of authors logins. Prevent visitors from collecting logins of the content authors from the website links (like example.com/?author=1). Also this function known as Stop User Enumeration.
- Prevent collecting of user login on password reset. The password reset error will not contain the data about selected username does not exist.
- Disable REST API for non-authenticated users. Turn this on to deny access to WordPress REST API for non-authenticated users. Denied requests will get a 401 HTTP Code (Unauthorized).
- Disable the WordPress endpoint “users” REST API. Disables access to /wp-json/wp/v2/users and /wp-json/wp/v2/users/”id_user”.
- Disable File Editor. By prohibiting file editing, you protect the site from malicious attacks that may try to change the code and gain access to the site or steal confidential information.
TRANSLATE INTO YOUR LANGUAGE
- Thank you for helping translate the plugin!
- 感谢您帮助翻译这个插件! (Gǎnxiè nín bāngzhù fānyì zhège chājìan!)
- प्लगइन का अनुवाद करने में मदद के लिए धन्यवाद! (Plugin ka anuvaad karne mein madad ke liye dhanyavaad!)
- ¡Gracias por ayudar a traducir el complemento!
- Merci d’avoir aidé à traduire le plugin !
- شكرًا لمساعدتك في ترجمة الإضافة! (Shukran limusaa’adatika fi tarjamat al-idafa!)
- প্লাগইন অনুবাদে সাহায্য করার জন্য ধন্যবাদ! (Plug-in onubade shahajjo korar jonno dhonnobad!)
- Спасибо за помощь в переводе плагина! (Spasibo za pomoshch v perevode plagina!)
- Obrigado por ajudar a traduzir o plugin! (Obrigada if female)
- پلگ ان کا ترجمہ کرنے میں مدد کرنے کا شکریہ! (Plug-in ka tarjuma karne mein madad karne ka shukriya!)
- Terima kasih telah membantu menerjemahkan plugin!
- Danke, dass du beim Übersetzen des Plugins geholfen hast!
- プラグインの翻訳を手伝ってくれてありがとうございます! (Puraguin no hon’yaku o tetsudatte kurete arigatou gozaimasu!)
https://translate.wordpress.org/projects/wp-plugins/security-malware-firewall/
Instalação
DEFAULT INSTALLATION
Here is a video guide with installation process or you can use the text version down below.
-
Download, install, and activate ‘Security by CleanTalk’.
-
Get Access key https://cleantalk.org/wordpress-security-plugin
-
Enter Access key in the settings WordPress console -> Settings -> Security by CleanTalk -> General settigns. Save Changes.
-
Go to Malware scanner tab and do the very first scan.
-
Done! The plugin is ready to use.
INSTALLATION FROM THIRD-PARTY SOURCE
- Download latest version on your computer’s hard drive,
https://downloads.wordpress.org/plugin/security-malware-firewall.zip
-
Go to your WordPress Dashboard->Plugins->Add New->Upload CleanTalk zip file.
-
Click Install Now and Activate.
-
After activated, go to plugin settings. Then you will need to create an API key, this is done automatically for you. Just click on “Get access key automatically”
Installation completed successfully.
Installation from wordpress.org directory
-
Navigate to Plugins Menu option in your WordPress administration panel and click the button “Add New”.
-
Type CleanTalk in the Search box, and click Search plugins.
-
When the results are displayed, click Install Now.
-
Select Install Now.
-
Then choose to Activate the plugin.
-
After activated, go to plugin settings. Then you will need to create an API key, this is done automatically for you. Just click on “Get access key automatically”
Installation completed successfully.
Log de Changes
2.192 Nov 06 2026
- Upd. Firewall. Adding private lists fixed.
- Fix. Settings. Child sites do not affect scanner/fswatcher settings and runtime.
- Fix. Scanner. Fixed signatures count during send results.
- Fix. Scanner. Cure. Loop cure fixed in case of unresponded request to external original source.
- Upd. Settings. Switch to react scan tab. (#764)
- Upd. Firewall. Improve fw check. (#763)
- Fix. Scanner. Memory exhaustion on important files listing with a huge debug.log
- Fix. Scanner. Module hashes update removes rows of other modules containing the slug
- Fix. Scanner. Module hashes are not inserted when the module has an approved file
- Fix. FSW. Restriction of access to FSW, edits for wpms, restriction for file actions (#762)
- Fix. 2FA. Flow updates. (#761)
- Fix. Settings. Fix notice appear on subsite on wpms. (#760)
- Upd. Cron. Interval mechanism for awakening task crowns
- Upd. Cron. Limiting the launch of Cron tasks
2.191 Oct 22 2026
- Fix. FSW. Restriction of access to FSW, edits for wpms, restriction for file actions (#762)
- Fix. 2FA. Flow updates. (#761)
- Fix. Settings. Links updated.
- Fix. Cure. Fixed cure regex errors before writing file contents.
- Fix. Scanner. Cure. Skip cure stage if option is currently disabled in settings.
- Fix. Scanner. Now manual scan starts correctly even if automatic scan option is disabled.
- Fix. Code. Optimizing the parsing of approved hashes https://app.doboard.com/1/task/57727
2.190 Oct 13 2026
- New. Security. Lost-password interface is under rate limit. (#755)
- Upd. BFP. Lost password interface protected. (#743)
- Upd. Scan. Switch to react scan accordions. (#756)
- Fix. Scanner. Cure. Fixed stub gluing.
- Fix. Code. Added the wp-element dependency
- Upd. Scan. Improve file system analysis. (#744)
- New. Plugins page. Show changelog in the update notice. https://app.doboard.com/1/task/46119
- Fix. Scanner. Cloud Analysis. Prevent infinite status polling. https://app.doboard.com/1/task/55892
- Fix. FW. Blocking the launch of parallel updates with Direct Upd https://app.doboard.com/1/task/58028
- Fix. HeuristicAnalyser. Remove is_callable check
2.189 Sep 25 2026
- Fix. Code. Re-minify JS.
- Fix. UI. Plugin tabs wrap to fit the screen. (#746)
- Upd. Security log. Actions buttons updated. (#749)
- Code. Merge conflict fixed.
- Fix. Code. React bundle rebuilt.
- Upd. Scan. Improve UX. (#750)
- Upd. Readme. Changelog updated.
- Upd. Version 2.189.
- Fix. Code. JS bundle rebuilt.
- Fix. JS. Settings dependencies fixed on initial load and state changes. (#741)
- Fix. Code. 2FA functionality fixed.
- Fix. User activity timeline. SVG height adjusted to display all event types.
- Upd. Scanner. Frontend controller removed. (#718)
- Fix. Settings. Added the action_shuffle_salts key for the render
- Upd. Firewall. Emergency bypass logic updated to token-via-email model. https://app.doboard.com/1/task/55234
- Upd. Settings. Update links on wpms to subsite settings. (#738)
- Fix. UploadChecker. Editing the condition for WP_Error https://app.doboard.com/1/task/56923
- New. Code. Auto tests banners. (#733)
- Fix. Code. Fixed compatibility with php8.5. (#734)
2.188 Sep 10 2026
- Fix. SecurityLog. Fixed ip column and timeline render. https://app.doboard.com/1/task/44430
- Upd. Settings. Improve admins counter on settings page. https://app.doboard.com/1/task/42426
- Upd. Firewall. Resolves the country by the smallest network. https://app.doboard.com/1/task/41240
- New. Settings. Server Requirements block. https://app.doboard.com/1/task/42654
- Code. Automate release. SVN auto-commit implemented. https://app.doboard.com/1/task/38415
- Fix. Automate release. Changelog adaptation, link duplicate removed. https://app.doboard.com/1/task/38415
- Fix. Automate release. Changelog adaptation. https://app.doboard.com/1/task/38415
- Fix. Sync. Resume cooldown extended form PSC cache warm. https://app.doboard.com/1/task/56074
- Upd. VulnerabilityAlarmService. Added current vulnerable module version support to sendReport(). https://app.doboard.com/1/task/56074
2.187 Aug 31 2026
- Fix. Code. Remove unused code after react implemented.
- Fix. RemoteCalls. Improve flow to exclude freezing on local wp environment.
- Fix. Scanner. No extension files detection fixed.
- Fix. Settings. Improve psc detect in plugins list.
- Fix. Settings. Improve template processing.
- Fix. UploadChecker. Edits when rendering results and selecting data.
- Upd. Settings. Links to research reports.
- Upd. Settings. Malware scanning new description.
- Upd. Scanner. Improve flow to reduce gathering unneeded data.
- Upd. Scanner. Binary analysis. Moved severity to suspicious. Description added.
Capturas de tela


Para desenvolvedores
Este é o seu plugin? Mostre os números.
Adicione um crachá ao vivo ao seu site, Documentos ou Readme do GitHub. Ele é atualizado por conta própria - nenhuma conta necessária.
Best Security Plugin, Firewall & M… alternatives
All 2FA plugins →



FAQ
Security Plugin, Firewall & Malware…: quick answers
Respostas diretas, extraídas de dados ao vivo WordPress.org.
Fonte: WordPress.org
Is Security Plugin, Firewall & Mal… free?
Yes. Security Plugin, Firewall & Mal… is free to download and use from the official WordPress.org plugin directory.
Is Security Plugin, Firewall & Mal… safe to use in 2026?
Yes — Security Plugin, Firewall & Mal… is a safe, well-maintained plugin to use in 2026. It runs on 40K+ sites, is rated 4.8/5 and was last updated 2 weeks ago, and scores 94/100 on our health check.
How many websites use Security Plugin, Firewall & Mal…?
Security Plugin, Firewall & Mal… is active on 40K+ WordPress websites and has been downloaded 3,135,473 times since it launched in August 2016. It was downloaded 67,224 times in the last 30 days.
Does Security Plugin, Firewall & Mal… work with WordPress 7.1?
Yes. The developer has tested Security Plugin, Firewall & Mal… up to WordPress 7.1.5, the latest release. It requires WordPress 5.0 or newer.
What PHP version does Security Plugin, Firewall & Mal… need?
Security Plugin, Firewall & Mal… requires PHP 7.2 or higher. Most hosts run PHP 8.x today, so it works on any modern WordPress hosting.
When was Security Plugin, Firewall & Mal… last updated?
The latest version, 2.192, was released on November 9, 2026 (2 weeks ago).
Who makes Security Plugin, Firewall & Mal…?
Security Plugin, Firewall & Mal… is developed and maintained by CleanTalk Inc.
What are the best alternatives to Security Plugin, Firewall & Mal…?
The most popular alternatives to Security Plugin, Firewall & Mal… are Wordfence Security (5M+ installs), Really Simple Security (3M+ installs) and Limit Login Attempts Securi… (1M+ installs).
Alimentado por PageForge
Um modelo e uma planilha. Uma página real para cada pesquisa.
PageForge Transforma cada linha de um CSV em uma página WordPress com seu próprio título, URL, SEO campos e esquema, construído no layout que você já desenhou. Gratuito em WordPress.org.
- CSV e XLSX, mais Google Sheets em Profissional e Empresarial
- Seu próprio título, URL, SEO campos e esquema para cada página
- Funciona com o editor de blocos, Elementor, Divi e Avada
- Gratuito em WordPress.org, sem cartão de crédito