


Limiter les tentatives de connexion
Limit the number of login attempts possible both through normal login as well as using auth cookies.

Utiliser avec prudence
Limit Login Attempts works, but test it on a staging site before relying on it in 2026. It runs on 200K+ sites, is rated 4.6/5 and was last updated 4 years ago, and scores 47/100 on our health check.
- Prouvé à grande échelle sur plus de 200 000 sites actifs
- Loved by users — 4.6/5 from 202 reviews
- Momentum — downloads up 42.5% vs the previous 30 days
- Pas de mise à jour dans 3 ans
- Uniquement testé jusqu'à WordPress 6,2 (le dernier est de 7,1)
Comment s'accumule-t-il ?
Côte à côte sur les installations, les mises à jour, les évaluations et le support
Téléchargements quotidiens
Les pics de téléchargement suivent généralement une nouvelle version - chaque site qui met à jour automatiquement compte comme un téléchargement.
Classements
Where Limit Login Attempts stands todayWordPress.org Classements de recherche
Position en direct dans la recherche de plugins, Top 100| Mot-clé | Position |
|---|---|
| authentication | >100 |
| login | >100 |
| la sécurité | >100 |
Adoption de version
Part de sites actifs par version.
Répartition des notes
★★★★★★★★★★ 4.6 from 202 reviews
About Limit Login Attempts
From the official readme · v1.7.2Description
Limit the number of login attempts possible both through normal login as well as using auth cookies.
By default WordPress allows unlimited login attempts either through the login page or by sending special cookies. This allows passwords (or hashes) to be brute-force cracked with relative ease.
Limit Login Attempts blocks an Internet address from making further attempts after a specified limit on retries is reached, making a brute-force attack difficult or impossible.
Traits
- Limit the number of retry attempts when logging in (for each IP). Fully customizable
- Limit the number of attempts to log in using auth cookies in same way
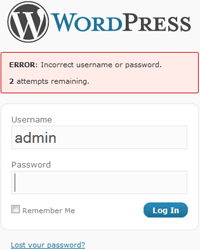
- Informs user about remaining retries or lockout time on login page
- Optional logging, optional email notification
- Handles server behind reverse proxy
- It is possible to whitelist IPs using a filter. But you probably shouldn’t. 🙂
Translations: Bulgarian, Brazilian Portuguese, Catalan, Chinese (Traditional), Czech, Dutch, Finnish, French, German, Hungarian, Norwegian, Persian, Romanian, Russian, Spanish, Swedish, Turkish
Plugin uses standard actions and filters only.
Installation
- Download and extract plugin files to a wp-content/plugin directory.
- Activate the plugin through the WordPress admin interface.
- Customize the settings on the options page, if desired. If your server is located behind a reverse proxy make sure to change this setting.
If you have any questions or problems please make a post here: https://wordpress.org/tags/limit-login-attempts
Journal de modifications
Users of version 1.6.2 and 1.7.0 should upgrade immediately. There was a problem with "auth cookie" lockout enforcement. Lockout of normal password login attempts still worked as it should. Please see plugin Changelog for more information.
1.7.2
Security fixes.
1.7.1
This version fixes a security bug in version 1.6.2 and 1.7.0. Please upgrade immediately.
“Auth cookies” are special cookies set at login that authenticating you to the system. It is how WordPress “remembers” that you are logged in between page loads.
During lockout these are supposed to be cleared, but a change in 1.6.2 broke this. It allowed an attacker to keep trying to break these cookies during a lockout.
Lockout of normal password login attempts still worked as it should, and it appears that all “auth cookie” attempts would keep getting logged.
In theory the “auth cookie” is quite resistant to brute force attack. It contains a cryptographic hash of the user password, and the difficulty to break it is not based on the password strength but instead on the cryptographic operations used and the length of the hash value. In theory it should take many many years to break this hash. As theory and practice does not always agree it is still a good idea to have working lockouts of any such attempts.
1.7.0
- Added filter that allows whitelisting IP. Please use with care!!
- Update to Spanish translation, thanks to Marcelo Pedra
- Updated Swedish translation
- Tested against WordPress 3.3.2
1.6.2
- Fix bug where log would not get updated after it had been cleared
- Do plugin setup in ‘init’ action
- Small update to Spanish translation file, thanks to Marcelo Pedra
- Tested against WordPress 3.2.1
1.6.1
- (WordPress 3.0+) An invalid cookie can sometimes get sent multiple times before it gets cleared, resulting in multiple failed attempts or even a lockout from a single invalid cookie. Store the latest failed cookie to make sure we only count it as one failed attempt
- Define “Text Domain” correctly
- Include correct Dutch tranlation file. Thanks to Martin1 for noticing. Thanks again to Bjorn Wijers for the translation
- Updated POT file for this version
- Tested against WordPress 3.1-RC4
1.6.0
- Happy New Year
- Tested against WordPress 3.1-RC1
- Plugin now requires WordPress version 2.8+. Of course you should never ever use anything but the latest version
- Fixed deprecation warnings that had been piling up with the old version requirement. Thanks to Johannes Ruthenberg for the report that prompted this
- Removed auth cookie admin check for version 2.7.
- Make sure relevant values in $_COOKIE get cleared right away on auth cookie validation failure. There are still some problems with cookie auth handling. The lockout can trigger prematurely in rare cases, but fixing it is plugin version 2 stuff unfortunately.
- Changed default time for retries to reset from 24 hours to 12 hours. The security impact is very minor and it means the warning will disappear “overnight”
- Added question to FAQ (“Why not reset failed attempts on a successful login?”)
- Updated screenshots
Captures d'écran
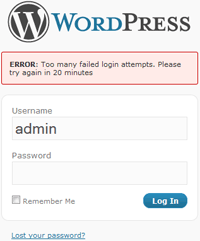
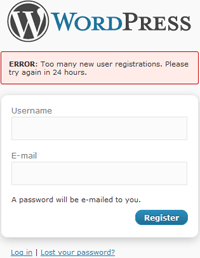
Pour les développeurs
Est-ce votre plugin ? Montrez les chiffres.
Ajoutez un badge en direct à votre site, docs ou github readme. Il se met à jour par lui-même - aucun compte n'est nécessaire.
Best Limit Login Attempts alternatives
All authentication plugins →
FAQ
Limit Login Attempts: quick answers
Réponses directes, extraites des données en direct WordPress.org.
Source : WordPress.org
Is Limit Login Attempts free?
Yes. Limit Login Attempts is free to download and use from the official WordPress.org plugin directory.
Is Limit Login Attempts safe to use in 2026?
Limit Login Attempts works, but test it on a staging site before relying on it in 2026. It runs on 200K+ sites, is rated 4.6/5 and was last updated 4 years ago, and scores 47/100 on our health check.
How many websites use Limit Login Attempts?
Limit Login Attempts is active on 200K+ WordPress websites and has been downloaded 2,318,393 times since it launched in January 2009. It was downloaded 8,451 times in the last 30 days.
Does Limit Login Attempts work with WordPress 7.1?
Limit Login Attempts is officially tested up to WordPress 6.2.16, while the latest release is 7.1.5. It may still work, but try it on a staging site first.
When was Limit Login Attempts last updated?
The latest version, 1.7.2, was released on April 4, 2023 (4 years ago).
Who makes Limit Login Attempts?
Limit Login Attempts is developed and maintained by Automattic.
What are the best alternatives to Limit Login Attempts?
The most popular alternatives to Limit Login Attempts are Two Factor (100K+ installs), WPS Limit Login (100K+ installs) and WP-Members Membership Plugin (50K+ installs).
Propulsé par PageForge
Un modèle et une feuille de calcul. Une vraie page pour chaque recherche.
PageForge transforme chaque ligne d'un CSV en une page WordPress avec son propre titre, URL, SEO et schéma, construit sur la mise en page que vous Déjà conçu. Gratuit sur WordPress.org.
- CSV et XLSX, plus Google Sheets sur les professionnels et les entreprises
- Son propre titre, URL, SEO champs et schéma pour chaque page
- Fonctionne avec l'éditeur de blocs, Elementor, Divi et Avada
- Gratuit sur WordPress.org, pas de carte de crédit